A risk register that stops at naming threats won’t prepare your business for an outage. An IT risk assessment template should record each risk, its likelihood and impact, the controls already in place, who owns it and what action will reduce it. ISO/IEC 27005 is a standard focused on information security risk management, according to the International Organization for Standardization.
An IT risk assessment template gives your team a consistent way to identify gaps and decide what needs attention. Its real value, though, is whether the assessment helps you respond when a critical system, supplier or data source becomes unavailable.
This guide covers what to include, how to assess and prioritise risks, and how to link findings to business impact analysis and disaster recovery planning. It also explains how to turn threats into clear responsibilities, mitigation actions and recovery priorities, so the assessment remains useful as circumstances change.
Key Takeaways
- Build a consistent record of technology risks, current safeguards, ownership and follow-up actions.
- Use business impact analysis to connect technology risks with the processes your organisation needs to keep running.
- Gather threat information across systems, people and suppliers to uncover risks a basic checklist might miss.
- Turn assessment findings into recovery priorities, assigned responsibilities and a plan you can revisit as your IT environment changes.
What Is an IT Risk Assessment Template?
An IT risk assessment template is a structured document for recording technology threats and decisions. ISO/IEC 27005 is a standard focused on information security risk management, according to the International Organization for Standardization. It supports a repeatable process: identify risks, analyse their likelihood and impact, then select responses.
An information security risk assessment focuses on threats to information and its confidentiality, integrity and availability. An IT risk assessment can have a wider scope, including systems, devices, suppliers, services and business operations. It might, for example, cover both unauthorised access to customer data and a network outage that disrupts sales.
Risk appetite is the level and type of risk an organisation is willing to accept while pursuing its objectives. Set out that boundary clearly, then compare each assessed risk with it. Responses may include reducing risk through controls, avoiding the activity, sharing or transferring some exposure, or accepting the risk with a named owner and documented rationale.
To create a free starting point, build a simple Excel workbook or Word document and tailor its fields to your systems. HSE example risk assessments can help with identifying hazards, but adapt any example to your own circumstances rather than copying it unchanged.
For each entry, record a reference ID, date raised, category, description, existing controls, owner, mitigation action and due date. Small businesses can start with essential services, business data, staff access and key suppliers. This keeps the assessment proportionate and grounded in day-to-day operations.
Review the assessment at least annually and whenever significant changes occur in the IT environment. UK GDPR and the NIS Regulations may also be relevant. Record which requirements apply, the systems involved and who owns follow-up. A generic template may overlook business-specific hazards or controls, leaving important risks unaddressed.
Risk assessments and business impact analyses
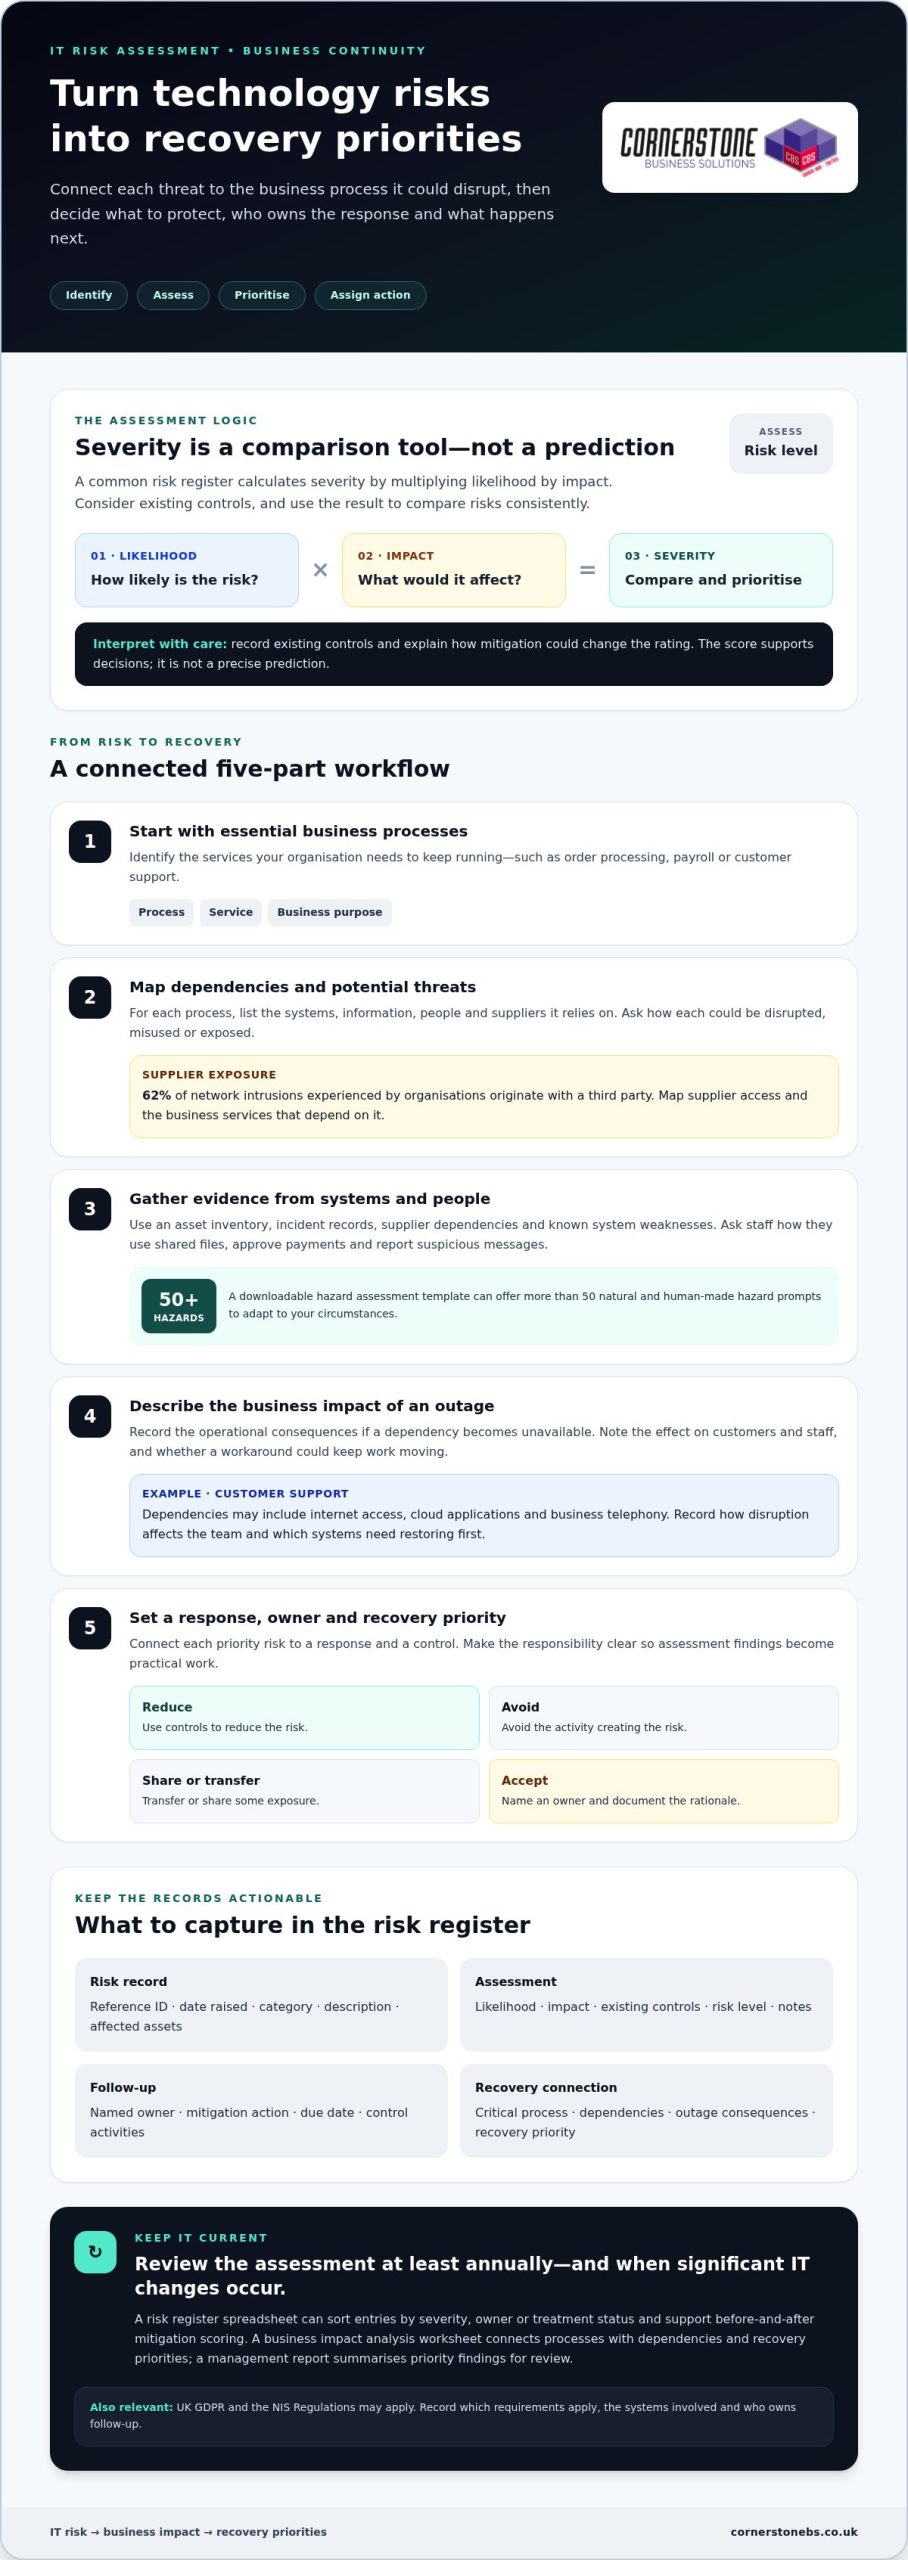
A business impact analysis identifies the processes your organisation needs to keep running. Start with services such as order processing, payroll or customer support. For each one, record its dependencies, including systems, information, people and suppliers. Then describe the operational consequences if a dependency becomes unavailable. This helps distinguish an inconvenience from a disruption that threatens essential work.
Use the analysis to set recovery priorities. For example, a customer support team may rely on internet access, cloud applications and business telephony. Record how an outage would affect customers and staff, which workaround could keep work moving, and which systems need restoring first. This connects technical risks to practical business decisions.
Assess each risk by considering its likelihood, impact and existing controls. A common register calculates severity by multiplying likelihood by impact. Use the result to compare risks consistently, not as a precise prediction. Record the risk level, control activities, owner and notes, then explain how mitigation could change the rating.
Choose tools that fit the decision you need to make:
- Risk register spreadsheet: Sorts risks by severity, owner or treatment status and supports before-and-after mitigation scoring.
- Business impact analysis worksheet: Connects critical processes with their technology dependencies, consequences and recovery priorities.
- FAIR analysis: Factor Analysis of Information Risk structures quantitative financial risk analysis around loss-event frequency and probable loss magnitude. Record assumptions so decision-makers can understand the estimate.
- Management report: Summarises priority findings and recommended mitigation activities for review and decision-making.
Keep the outputs connected. If a risk threatens a process identified as critical, the report should explain the response and the control that reduces exposure. A communication dependency map can also include business phone systems, helping teams consider how disruption could affect customer contact.
Start with an asset inventory: list devices, applications, data, user accounts and important suppliers. Then ask how each could be disrupted, misused or exposed. A downloadable hazard assessment template can include more than 50 potential natural and human-made hazards, offering prompts to adapt. Add relevant examples, such as a power failure affecting a server or a compromised account accessing business files.
Gather threat information from the people closest to each system. Ask staff how they use shared files, approve payments and report suspicious messages. Review incident records, supplier dependencies and known system weaknesses. Third parties deserve attention: 62 percent of network intrusions experienced by organisations originate with a third party. Map supplier access and record which business services depend on it.
Use practical tools to organise the evidence:
- Asset inventory: Connects each system or information asset to its owner, users and business purpose.
- Threat register: Records the reference ID, date raised, risk category and description, then links each threat to affected assets.
- Network diagram: Shows how devices, applications and external connections relate, helping identify shared points of failure.
- CIS Critical Security Controls: The Center for Internet Security has developed 18 standards, useful as a structured reference when reviewing security safeguards.
Turn each finding into an action, not just a label. If a supplier account can access sensitive files, for example, record the access involved, the information affected, existing safeguards and the person responsible for reducing exposure. Distinguish a confirmed weakness from a possible threat, and note the evidence behind each assessment. This makes future reviews more useful.
Compare the threat list with your organisation’s actual technology and working practices. Remove irrelevant prompts, add overlooked dependencies and record changes, such as a new cloud application or supplier connection. A tailored register helps decision-makers see which risks need investigation, mitigation or monitoring.
Using an IT risk assessment template in disaster recovery planning
A disaster recovery plan needs more than a list of threats. Use assessment findings to decide what must be restored, in what order and by whom. For each critical service, link the identified risks to technology dependencies, recovery steps and an accountable owner. If a cyber incident affects shared business files, for example, identify the affected service and who is responsible for restoring access.
Set recovery priorities according to business impact. Record which processes rely on each system, what an outage would mean and which workaround could support essential work. Define recovery time objectives, the target time for restoring a service, and recovery point objectives, the acceptable point to which data must be restored. These targets help teams choose practical recovery actions.
Use focused planning tools to turn findings into operational guidance:
- Recovery runbook: Sets out the sequence of recovery tasks, system dependencies and responsible roles.
- Dependency map: Shows which applications, devices, data and suppliers support each critical process.
- Risk register: Links recovery actions to specific threats, controls, owners and progress notes.
- Dashboard report: A Gantt-style timeline can track tasks, while pie charts can show action status and risk percentages.
Test the plan with a realistic scenario, such as a cloud application becoming unavailable. Ask each owner to follow the documented steps, identify missing access or instructions, and record where handovers fail. Update the assessment and runbook with those findings. Disaster recovery teams should update assessment results periodically to identify changes in risks.
The practical takeaway is to keep recovery planning connected to the risk register, not in a separate document that becomes stale. Review changes to systems, suppliers and business processes, then adjust priorities and assigned actions. If you need support turning risk findings into a workable recovery approach, discuss disaster recovery planning with a technology team.
Cornerstone Business Solutions: Managed IT Support
Cornerstone Business Solutions helps businesses turn risk assessment findings into practical action through Managed IT Support and Cyber Security. Turn to the team when technology risks need ongoing attention, security controls need strengthening, or your organisation needs support maintaining its IT environment.
Clear ownership matters. Work together to connect identified risks with the right priorities, whether that means reviewing user access, addressing system vulnerabilities or improving how your business uses Microsoft 365. Business Mobile can also be part of the discussion when staff need reliable ways to stay connected.
A well-maintained risk assessment gives your team a stronger foundation for informed decisions. If you’d like to discuss your IT needs, contact Cornerstone Business Solutions.
Make your next risk decision actionable
Make your IT risk assessment template part of regular decision-making, rather than a document that sits untouched. Assign someone to review it when business priorities or technology change, and make sure decisions reach those responsible for acting. This keeps risk management connected to how your organisation works.
If you need help putting that process into practice, Cornerstone Business Solutions offers Managed IT Support, Microsoft 365 and Cyber Security. The team can work with you to align your technology priorities with your business needs and keep the assessment useful as those needs evolve.
Start with one practical improvement, such as clarifying ownership of a key risk. An IT risk assessment template can help your team keep that action visible. Contact Cornerstone Business Solutions to discuss a next step for your business.
Frequently Asked Questions
What should an IT risk assessment template include?
Include enough context to understand each risk and make a decision. Alongside its description and rating, capture the affected business function, supporting evidence, review date and current status. For example, link a suspected account compromise to the relevant service and incident records. A clear version history also helps reviewers understand what changed and why.
How do you conduct an IT risk assessment step by step?
Conduct the assessment by setting a scope, gathering evidence, evaluating exposures, agreeing responses and recording decisions. Start with a defined area, such as remote access or finance systems. Speak with the staff who use it, review relevant records and identify scenarios that could interrupt work. Assign follow-up actions, then share the findings with those responsible for business continuity.
How do you score IT risks using likelihood and impact?
Score likelihood and impact against written criteria that your team applies consistently. For likelihood, explain the evidence supporting the rating, such as repeated alerts or a known weakness. For impact, consider the effects on customers, staff, operations and information. Keep the reasoning alongside the score: without a rationale, a rating can suggest false precision and make comparisons unreliable.
What are common IT risks to include in an assessment?
Include risks that reflect your organisation’s systems and working practices. Examples include phishing that leads to stolen credentials, incorrect access permissions that expose confidential files, lost devices containing business information, and software misconfiguration that disrupts a service. Consider human error and technology failure as well as deliberate attacks. Ask how each scenario could affect a specific team’s ability to work.
What UK laws and regulations affect IT risk assessments, including UK GDPR and NIS Regulations?
UK GDPR and the NIS Regulations may affect your organisation’s risk assessment. Record which requirements are relevant, the systems involved and who owns follow-up.
Where can I download a free IT risk assessment template in Excel or Word?
For a free starting point, create a simple workbook in Excel or a document in Word, then tailor its fields to your systems.
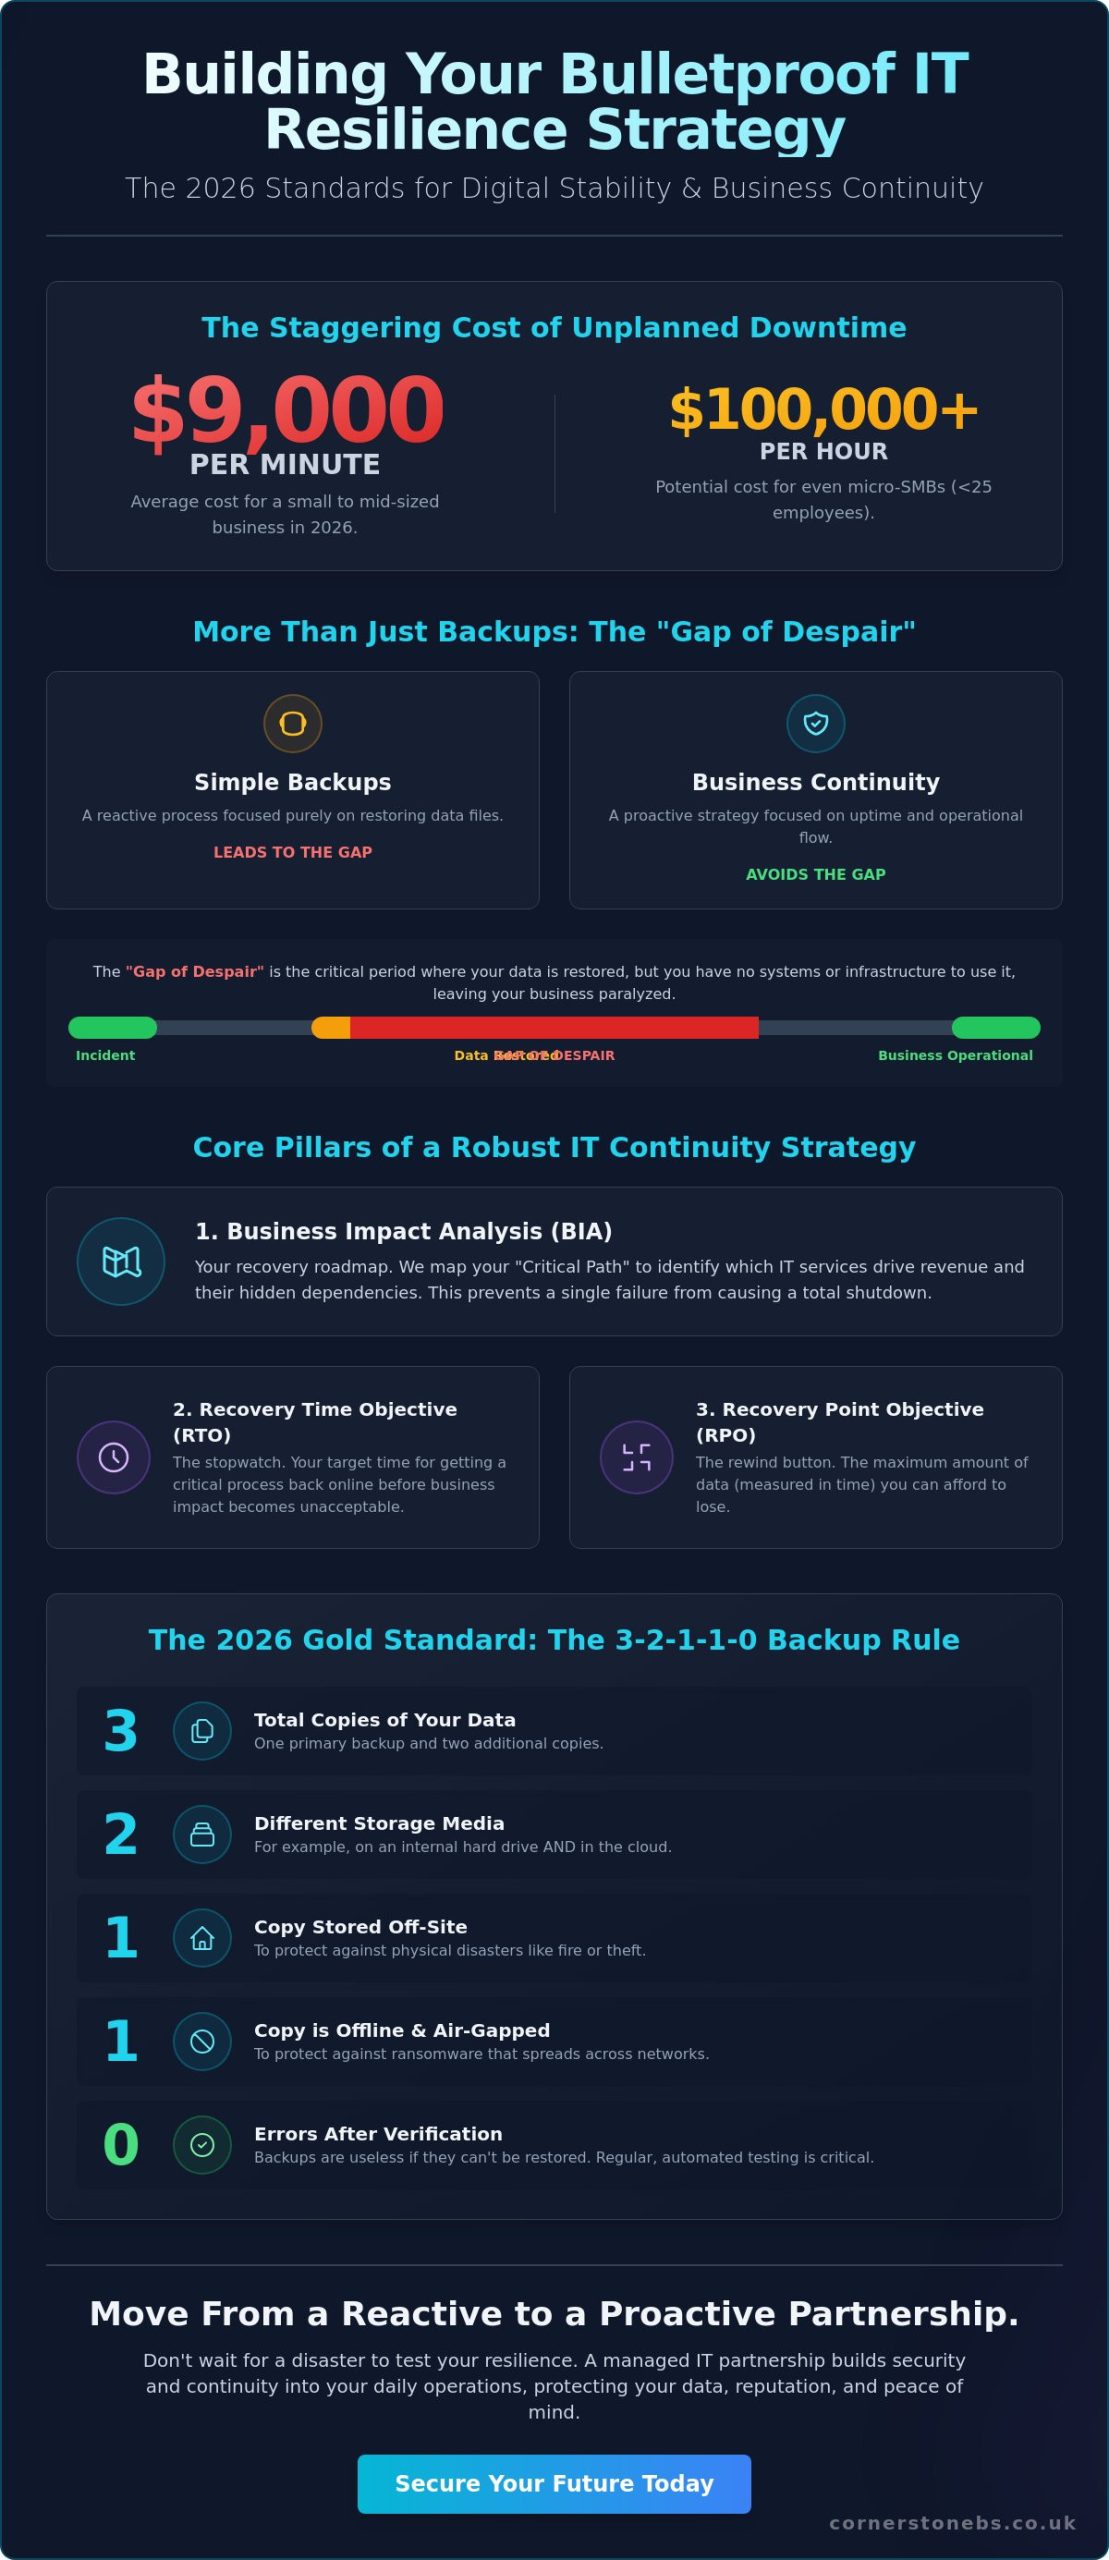
Did you know that for a small to mid-sized business in 2026, a single minute of unplanned downtime costs an average of $9,000? It’s a staggering figure that proves why reactive recovery is no longer enough to protect your livelihood. We know the knot in your stomach that forms when you think about a cyber attack or a sudden system failure. As your local technology partners, we’ve seen how easy it is to feel overwhelmed by the difference between simple backups and a comprehensive business continuity planning IT strategy. You want your business to be resilient, not just lucky.
You’ve likely already realized that your IT isn’t just a department; it’s the nervous system of your entire operation. This guide provides the clear, actionable roadmap you need to build a bulletproof resilience strategy that protects your data and your reputation. We’ll walk you through the 2026 standards for digital stability, from the new 3-2-1-1-0 backup rule to the latest ISO 22301 and DORA compliance requirements. You’ll learn exactly how to minimize downtime and ensure your business remains steady, even during a major disruption.
Key Takeaways
- Learn why modern business continuity planning IT must evolve to protect against complex cloud and supply chain risks rather than just local server failures.
- Identify your most critical operations by conducting a Business Impact Analysis to determine exactly how long your systems can afford to be offline.
- Clarify the vital difference between keeping your business moving during a crisis and the technical process of restoring data through disaster recovery.
- Build a more resilient infrastructure by identifying single points of failure and implementing secure, redundant cloud solutions for your team.
- Move from a reactive “break-fix” mindset to a proactive partnership that prioritizes long-term operational security and your peace of mind.
Defining Business Continuity Planning in an IT-First World
In 2026, your business is a digital entity. Every client interaction, every sale, and every project relies on a stable technology stack. Business continuity planning for IT is the strategic framework that ensures your critical digital functions remain available during and after a disaster. It isn’t just a safety net; it’s the architecture of your survival. While disaster recovery focuses on fixing what’s broken, business continuity planning IT focuses on keeping the lights on so your customers never even notice a problem. It’s the difference between a temporary hiccup and a permanent closure.
The risks have shifted dramatically over the last few years. We’ve moved away from the era where a “disaster” meant a fire in the server room. Today, your risks are distributed across the cloud and your global supply chain. If a third-party software provider suffers an outage, your operations could grind to a halt. Relying on a “good enough” approach is a dangerous game. Simple backups are no longer a viable continuity strategy because they don’t address the speed of modern business. If it takes you three days to restore from a backup, your reputation may already be beyond repair. Resilience is now a competitive advantage that builds deep trust with your clients. They need to know that your service is unshakeable, regardless of the digital weather.
The 2026 Threat Landscape for UK Businesses
The threats facing UK firms have become incredibly sophisticated. We’re seeing AI-driven ransomware that can scan for vulnerabilities faster than any human, alongside social engineering tactics that are nearly impossible to spot. The rise of hybrid work has also expanded the attack surface. You now have to worry about securing the “home office” link just as much as your central office. Digital resilience is the ability to absorb, adapt, and evolve through disruption.
Why ‘Business Continuity’ is More Than Just ‘Backups’
It’s easy to fall into the trap of thinking your daily backup has you covered. It doesn’t. Backups are purely about data; continuity is about uptime and operational flow. We often talk about the “Gap of Despair.” This is the period where you have your data back, but you have no systems, hardware, or network infrastructure to run it on. You’re stuck with files you can’t use. This is where proactive managed IT services make the difference. By building resilience into your daily operations, we ensure that your business stays agile and ready for anything. We don’t just protect your data; we protect your ability to do business.
The Core Pillars of a Robust IT Continuity Strategy
Building a resilient business isn’t about buying every piece of software on the market. It’s about knowing exactly which parts of your setup keep your doors open. Effective business continuity planning IT starts with a cold, hard look at your operations. You need to identify which systems are the heartbeat of your company and which ones can wait a few hours if things go wrong. We help you move away from guesswork and toward a strategy built on data and clear priorities.
Performing a Business Impact Analysis (BIA)
A BIA is your roadmap for recovery. It maps your “Critical Path,” which is the sequence of IT services that drive revenue right now. For many of our local partners, this means looking at the hidden links between their CRM, email, and Business VoIP systems. If your phone lines go down, can you still take orders? If your CRM is offline, does your sales team stop dead? Identifying these dependencies prevents a small glitch in one area from cascading into a total business shutdown.
Setting Realistic Recovery Objectives (RTO & RPO)
Once you know what’s critical, you have to set your targets. These are known as Recovery Time Objectives (RTO) and Recovery Point Objectives (RPO). RTO is your stopwatch; it’s the target time for getting a process back online before the consequences become unacceptable. RPO is your rewind button; it’s the maximum amount of data you can afford to lose. For example, losing five minutes of data might be fine for a local retailer, but it could be catastrophic for a financial firm.
There’s always a trade-off between recovery speed and cost. Finding the “Sweet Spot” for your SME is essential. While an RTO of zero is technically possible through high-end failover systems, it’s often financially impractical for most firms. This is why leadership must agree on these targets. It’s a business decision, not just an IT one. Integrating these objectives into a formal IT Disaster Recovery Plan ensures everyone knows the goal when pressure is high. If you’re unsure where your single points of failure are, our Managed IT Support team can help you audit your current setup to find the gaps and strengthen your business continuity planning IT efforts.
Business Continuity vs. Disaster Recovery: Understanding the Difference
Many business owners use the terms “Business Continuity” and “Disaster Recovery” interchangeably, but they serve very different roles in your resilience strategy. Confusing the two is a common mistake that can lead to a false sense of security. If you only have a recovery plan, you might find yourself with restored data but no way to actually use it. Effective business continuity planning IT ensures that these two elements work in harmony. While one focuses on the technology, the other focuses on the survival of the business itself.
Think of it as a timeline of events. Business continuity starts the very moment a disruption is detected. It’s the immediate response that keeps your team productive. Disaster recovery, on the other hand, typically starts once a “disaster” has been officially declared and the focus shifts to rebuilding. Having a robust layer of cyber security services is your first line of defense, often preventing the need for disaster recovery altogether by stopping threats before they cause a shutdown. When prevention fails, you need both the playbook to keep working and the toolbox to fix the systems.
Strategic Planning vs. Tactical Execution
Business continuity is your strategic “Playbook.” It outlines the people, processes, and communication channels required to keep the business moving. For example, if your office becomes inaccessible, your business continuity plan might involve immediately redirecting staff to remote desktops so they can continue serving clients. Disaster recovery is your tactical “Toolbox.” It’s the technical process of restoring servers, networks, and data from your backups. You need the playbook to know what to do and the toolbox to get back to a state of normality.
Overcoming the ‘Too Small to Fail’ Misconception
We often hear smaller firms say they don’t need complex planning because they aren’t a global enterprise. In reality, SMEs are often more vulnerable to downtime. A large corporation can absorb a few days of disruption; a local business might never recover from the reputational damage. Small business IT environments frequently suffer from the “Single Point of Failure” trap, where one broken switch or a single compromised password can take down the whole operation. The good news is that you don’t need an enterprise budget to stay safe. Simplified business continuity planning IT frameworks can provide 80% of the protection for a fraction of the cost, ensuring your local business remains stable and reliable for your customers.
Steps to Implementing a 2026-Ready IT Continuity Plan
Building a resilient business isn’t a one-off project. It is a continuous cycle of improvement. Now that you understand the pillars of business continuity planning IT, it’s time to put those concepts into action. A 2026-ready plan focuses on agility and the reality of a cloud-first world. We follow a clear five-step process to ensure your operations are protected from the ground up.
Auditing Your Infrastructure for 2026 Risks
Your first step is a thorough audit of your current hardware and connections. We often look at the “Last Mile” of your internet connectivity. If your primary fiber line is cut, do you have a secondary connection that kicks in automatically? Network outages account for 31% of IT service interruptions, so redundancy here is vital. Even though many services have moved to the cloud, local power protection still matters. Uninterruptible Power Supplies (UPS) and battery backups ensure your local hardware stays safe during a surge or outage. Finally, evaluate your third-party vendor risks. If your SaaS providers or IT suppliers suffer a breach, you need to know how that impacts your own ability to serve clients.
Redundancy and Failover in the Cloud
The second step is designing for redundancy using modern cloud solutions. In 2026, we leverage tools like Microsoft 365 as a foundational continuity tool. Since your data is stored in the cloud, your team can work from any location with an internet connection. For more complex setups, we use Azure Site Recovery to automate the failover of your virtual servers. This ensures that if one data centre goes offline, your systems stay live in another. Geographic redundancy is no longer an enterprise-only luxury; it’s a standard requirement for any business that values its uptime.
Once your infrastructure is secure, you must document the plan. This playbook defines who does what, when, and how during an incident. It eliminates confusion when stress levels are high. However, a document on a shelf isn’t enough. You must train your team and simulate regular “Fire Drills” for your IT systems. These simulations allow us to test your failover mechanisms without causing actual downtime. Finally, review and evolve your plan. As you add new technology or your team grows, your business continuity planning IT strategy must adapt to stay effective. If you want to ensure your setup is truly bulletproof, we invite you to start a conversation with our local experts today.
Partnering for Resilience: How Managed IT Secures Your Future
The old days of the “break-fix” model are gone. Waiting for a system to fail before calling for help is a recipe for disaster in a world where every minute of downtime drains your revenue and damages your reputation. We’ve moved toward a model of proactive resilience. This means we don’t just fix problems; we prevent them from happening in the first place. By integrating business continuity planning IT into every IT company solution we provide, we ensure your business remains stable, secure, and ready for growth.
Many business owners find that their in-house teams are often overstretched, focusing on daily tickets rather than long-term strategy. Partnering with a team of outsourced experts provides you with a depth of knowledge and a range of specialized tools that are difficult to maintain internally. We act as your dedicated technology partner, providing the high-level oversight needed to keep your operations running smoothly. You gain the peace of mind that comes from knowing your digital infrastructure is in the hands of professionals who care about your success as much as you do.
The Role of Proactive Monitoring and Maintenance
Our approach centers on constant vigilance. We use advanced monitoring systems to identify hardware failure “pre-symptoms” long before they cause an actual outage. If a drive is starting to lag or a server is running hot, we catch it and resolve it during scheduled maintenance. Automated patching serves as your first line of defense, closing security gaps before they can be exploited by continuity-threatening breaches. Industry data suggests that proactive maintenance reduces emergency repair costs by up to 50%. This proactive stance keeps your budget predictable and your systems reliable.
Choosing a Long-Term Technology Partner
When you look for a partner to manage your resilience, credentials matter. You want a team with a proven track record and multi-award-winning expertise. We’re proud of our regional roots and our global partnerships with industry giants like Cisco, Microsoft, and IBM. These relationships allow us to bring enterprise-grade technology to local businesses with a personal, approachable touch. We don’t believe in one-size-fits-all packages. Every business has a unique risk profile, and your business continuity planning IT strategy should reflect that.
Future-Proof Your Business with Digital Resilience
Resilience is no longer a luxury for the few. It is a fundamental requirement for every local firm. We’ve mapped out how a thorough Business Impact Analysis and clear recovery objectives protect your revenue. By embracing a cloud-first approach and eliminating single points of failure, you turn potential disasters into manageable events. A proactive business continuity planning IT framework doesn’t just save data; it saves your reputation and your peace of mind.
You don’t have to face these technical challenges alone. As a multi-award-winning IT provider and official partner with Microsoft, IBM, and Cisco, we bring world-class expertise to our regional community. Our 24/7 proactive system monitoring works behind the scenes to keep your network stable and secure. Book a free IT resilience audit with our award-winning experts today to start your journey toward total digital stability. We’re ready to help you build a stronger, more resilient future.
Frequently Asked Questions
What is the difference between business continuity and disaster recovery?
Business continuity is your broad strategy for keeping the entire organization operational during a crisis, focusing on people, processes, and communication. Disaster recovery is a specific subset of that plan that deals with the technical restoration of your IT systems and data. You need the strategic playbook of continuity to ensure your team knows how to work while the tactical tools of recovery get your servers back online.
How much does a business continuity plan cost to implement?
The cost varies significantly based on the size of your business and the complexity of your digital infrastructure. We recommend viewing this as an investment in your company’s survival rather than a standard expense. A well-designed business continuity planning IT strategy is built to prevent the staggering costs of downtime, which can reach $1,670 per minute for micro-businesses and much more for larger firms.
Does my business need a BCP if all our data is in the cloud?
Yes, because being in the cloud doesn’t make you immune to service outages or data loss. While cloud providers manage the underlying hardware, you’re still responsible for managing your data and ensuring your team can access it if a specific platform goes down. A robust plan accounts for cloud-to-cloud backups and alternative access methods to keep your operations moving if your primary provider has a hiccup.
How often should we test our IT business continuity plan?
You should test your plan at least once a year, or whenever you make a significant change to your technology stack. Regular “fire drills” ensure that your failover mechanisms actually work and that your team remembers their roles under pressure. Testing allows us to identify and fix gaps in a controlled environment before a real emergency occurs, ensuring your resilience remains high as your business evolves.
Can a managed IT provider write our business continuity plan for us?
A managed IT provider acts as a dedicated partner to help you design and document the technical side of your plan. While we handle the infrastructure, redundancy, and recovery logistics, we collaborate closely with your leadership team to align these solutions with your specific business goals. This partnership ensures your technical resilience supports your actual operational needs without creating unnecessary complexity.
What are the most common causes of IT downtime in 2026?
Network outages are a leading cause of disruption, accounting for 31% of all IT service incidents. However, human error remains the most significant factor, contributing to between 66% and 80% of all downtime events. These figures show why your business continuity planning IT efforts must focus on both technical redundancy and comprehensive staff training to be truly effective.
Is a business continuity plan a legal requirement for UK businesses?
It depends on your industry, but regulations are becoming much stricter. For example, the Digital Operational Resilience Act (DORA) took effect in January 2025, mandating robust resilience planning for the financial sector. Many other industries must follow ISO 22301:2019 standards to meet insurance requirements or maintain specific professional certifications. You should check your industry-specific guidelines to ensure you stay compliant.
How does cyber security fit into a business continuity strategy?
Cyber security is your first line of defense, designed to stop the disruptions that would otherwise trigger your continuity plan. By implementing strong protections, you reduce the likelihood of needing to use your recovery tools. When a breach does occur, your continuity strategy provides the roadmap to isolate the threat and keep your business running while your security team resolves the incident.