Posted on: August 31st, 2026 by Cornerstone
What if your next major contract is currently stalled on a procurement officer’s desk, simply waiting for proof of your security credentials? In 2026, iso 27001 compliance for uk businesses has shifted from a competitive edge to a non-negotiable requirement for entering enterprise supply chains. You’ve likely felt the mounting pressure from clients to demonstrate your certification, yet the prospect of managing the 93 Annex A controls while maintaining your daily operations can feel like an impossible balancing act.
We know the concern that the high costs and time commitment of iso 27001 compliance for uk businesses might seem daunting, particularly when you’re already stretched thin. This strategy guide clarifies the complexities, offering a practical roadmap to secure your sensitive data and successfully navigate rigorous UK tenders. You’ll discover the genuine ROI of certification and learn how a proactive approach to iso 27001 compliance for uk businesses builds a resilient framework that supports your long-term growth. We’ll preview the essential technical pillars and show you how to find a partner to handle the complex infrastructure requirements.
Key Takeaways
- Understand why 2026 is a pivotal year for updating your Information Security Management System to the latest 2022 standard.
- Master the 93 Annex A controls to streamline iso 27001 compliance for uk businesses and secure your digital infrastructure.
- Position your organisation to win lucrative UK public sector tenders by proving your commitment to robust data security.
- Follow a clear roadmap from initial gap analysis to proactive risk treatment to ensure a successful audit.
- Explore how managed services automate technical maintenance, providing the continuous evidence needed to sustain your certification.
What is ISO 27001 Compliance for UK Businesses in 2026?
Understanding What is ISO/IEC 27001? provides the foundation for your entire security strategy. It’s the globally recognised standard for an Information Security Management System (ISMS). While the 2013 version served the industry for a decade, the transition period officially ended in autumn 2025. This makes 2026 the first year where every new certification or renewal must align with the ISO/IEC 27001:2022 update. This version is specifically designed to address modern threats, focusing heavily on cloud security and complex supply chain risks.
We define an ISMS as a living framework of people, processes, and technology that evolves alongside your business risks. It’s not a static folder on a server; it’s the digital backbone of your organisation.
The Three Pillars of Information Security
Every control within the framework supports three core goals, often called the CIA triad. Balancing these ensures your security doesn’t get in the way of your productivity.
- Confidentiality: This ensures that only authorised users can access sensitive information. We help you implement strict access controls so your data stays in the right hands.
- Integrity: This protects your data from being altered or deleted by unauthorised parties. It’s about ensuring the information you rely on is accurate and untampered with.
- Availability: Security is useless if you can’t get to your data. This pillar ensures your IT systems are reliable, resilient, and accessible whenever your team needs them.
ISO 27001 vs. Cyber Essentials: Which Does Your Business Need?
Cyber Essentials is a fantastic starting point for any UK business. It focuses on basic technical controls like firewalls, secure configuration, and patch management. It’s your “digital front door” security. ISO 27001 is far more comprehensive. It moves beyond technical fixes to look at how your management team handles risk, training, and continuous improvement.
The Core Requirements of the ISO 27001:2022 Framework
Risk assessment sits at the very centre of the framework. It’s the pulse that keeps your security strategy relevant and effective. Instead of blindly applying every rule, you evaluate your specific threats and decide how to treat them. This proactive approach is what makes iso 27001 compliance for uk businesses so powerful; it’s tailored to your unique risks. The standard is split into two distinct parts: the mandatory management clauses (4-10) and the Annex A controls.
Clauses 4 through 10 establish the “Management” in Information Security Management System. They require your leadership to show commitment, set clear objectives, and provide the necessary resources to keep data safe. You’ll also need to prove you’re evaluating your performance and constantly looking for ways to improve your defences. It’s about building a culture of security, not just a list of rules.
Then come the 93 Annex A controls. These are the practical safeguards you put in place to mitigate risks. The 2022 update simplified these into four clear categories: Organisational, People, Physical, and Technological. For a deeper look at the transition to these updated controls, the BSI guide to ISO 27001 certification offers excellent technical detail on the international expectations for modern businesses.
Defining Your ISMS Scope
You must decide exactly which parts of your business the certification covers. This is your “scope.” If your scope is too narrow, you might fail to satisfy a client who wants to see your entire operation secured. If it’s too broad, you’ll spend more time and money than necessary. Modern cloud solutions have changed the game here. They often blur the lines of your traditional network perimeter, meaning you must carefully define where your responsibility ends and your provider’s begins.
The Statement of Applicability (SoA) Explained
The SoA is the most vital document during an audit. It lists every Annex A control and states whether it applies to your business. If you exclude a control, you must justify why. For example, if your team works entirely remotely, you might exclude certain physical controls related to on-site data centres. It’s not a “set and forget” document. It requires continuous documentation to prove you’re still managing those risks effectively as your business grows.
Keeping your SoA up to date can feel like a full-time job. Our managed IT support ensures your technical documentation stays current, so you’re always ready for an auditor’s visit.
Why UK Businesses Prioritise ISO 27001 Compliance
We’ve seen that businesses with a robust Information Security Management System (ISMS) recover faster from incidents. They have a clear plan, defined roles, and a roadmap for continuity. This level of preparation turns a potential disaster into a managed event, protecting your reputation when it matters most.
Financial Resilience and Risk Mitigation
Let’s talk about the bottom line. The cost of a data breach for a UK SME can be devastating. Beyond the immediate technical recovery, you face legal fees, loss of reputation, and potential fines. Implementing the standard provides a framework to meet and exceed UK GDPR requirements. For official guidance on these obligations, the ICO’s Guide to Data Security is the essential resource for understanding the “security principle” of data protection. It bridges the gap between legal necessity and technical excellence.
Investing in compliance builds long-term stability. It ensures your team follows repeatable, secure processes that protect your most valuable assets. This proactive stance can also lead to direct savings on professional indemnity and cyber security services insurance premiums. Insurers are much more likely to offer better rates to companies that can prove they have a robust, audited ISMS in place. Protecting your client confidentiality is no longer just a defensive move; it’s a proactive growth strategy that secures your future.
A Step-by-Step Roadmap to Achieving ISO 27001 Compliance
- Phase 1: Gap Analysis. We identify exactly where your current security posture fails to meet the standard’s 93 controls.
- Phase 2: Risk Assessment & Treatment. You decide how to handle identified threats, whether that’s through technical fixes, insurance, or process changes.
- Phase 3: Documentation & ISMS Build. This is where we create the policies and technical evidence needed to satisfy an auditor.
- Phase 4: Internal Audit. A vital “dress rehearsal” where you test your own systems to find flaws before the official visit.
- Phase 5: External Audit. The final Stage 1 (documentation review) and Stage 2 (evidence of practice) certification process.
Conducting a Meaningful Gap Analysis
You can’t fix what you haven’t found. Relying on internal guesswork often leads to “blind spots” that cause audit failures. We recommend using a professional eye to compare your current it company solutions against the rigorous Annex A controls. This phase gives you a realistic timeline for remediation. It ensures you don’t waste resources on unnecessary tools, focusing instead on the specific gaps that matter most to your business continuity.
Preparing for the Stage 1 and Stage 2 Audits
The external audit is a two-part evaluation. Stage 1 is a high-level review to ensure your ISMS is designed correctly. Stage 2 is the deep dive. The auditor will ask for proof that your team actually follows the policies you’ve written. If they find “non-conformities,” see them as a roadmap for improvement rather than a failure. Certification is a three-year cycle, requiring annual surveillance visits to ensure your standards don’t slip. It’s a commitment to being better every single day.
Our experts are here to handle the technical heavy lifting, ensuring your systems are audit-ready from day one. Let’s start building your resilient information security framework today.
How Managed IT Support Simplifies ISO 27001 Maintenance
Maintaining iso 27001 compliance for uk businesses shouldn’t be a manual burden for your internal team. While the audit focuses heavily on your policies, those policies only hold weight if your technical infrastructure supports them every single day. This is where managed support transforms from a utility into a strategic partnership. We provide the “continuous logging” and proactive monitoring required by Annex A, ensuring you have a digital paper trail for every event on your network. It’s about having the right evidence ready before an auditor even asks for it.
Technical Controls and Evidence Collection
Auditors don’t just want to hear about your security; they want to see the data. Our Managed IT services generate the granular reports needed to prove your multi-factor authentication (MFA) and encryption protocols are active. We take the heavy lifting of technical documentation off your shoulders. Instead of your staff spending hours pulling logs, we provide a streamlined stream of evidence. This allows your team to focus on their core roles while we maintain the technical backbone of your iso 27001 compliance for uk businesses.
The Role of Professional Services in Remediation
Sometimes, the initial gap analysis reveals that your legacy network infrastructure isn’t up to the task. We use professional services to overhaul your systems, ensuring they meet the rigorous standards of the 2022 framework. This often involves implementing robust cloud backup solutions as part of a comprehensive disaster recovery plan. Business continuity is a core requirement of the standard, and we ensure your data is recoverable even in a worst-case scenario. We don’t just find the problems; we build the solutions that keep you compliant.
We’re proud to act as the technical engine for our clients’ success. Contact Cornerstone for a friendly, no-pressure consultation on how our bespoke technology solutions support your compliance goals. Let’s have a conversation about securing your business for the long term.
Building a Secure Future for Your Business
As the digital landscape evolves, staying ahead of security threats is no longer optional. We’ve explored how the transition to the 2022 standard and the new Data (Use and Access) Act 2025 have reshaped the requirements for iso 27001 compliance for uk businesses. By following a structured roadmap and leveraging technical automation, you can transform a complex audit into a repeatable, efficient process that wins tenders and protects your reputation. It’s about more than just a certificate; it’s about the stability of knowing your data is safe.
Our multi-award-winning cyber security expertise ensures your organisation isn’t just following rules but building genuine resilience. We provide bespoke technology solutions tailored to UK compliance standards, backed by proactive managed IT support for long-term resilience that handles the technical evidence so you don’t have to. We’re proud to act as a dedicated partner for our clients, simplifying the technical heavy lifting so you can focus on growth.
Secure your business and start your journey to ISO 27001 compliance with Cornerstone today. We’re here to help you turn security into your strongest competitive advantage and look forward to having a conversation about your specific needs.
Frequently Asked Questions
How much does ISO 27001 compliance cost for a UK business?
External certification fees from UKAS-accredited bodies typically range between £6,800 and £10,000 for a small UK business in 2026. The total investment depends on your organisation’s size and current technical maturity. While these audit fees are paid to the certifying body, you also need to account for the internal resources or professional support required to build your framework. We focus on providing the robust technical infrastructure that ensures you’re ready for that investment.
How long does it take to become ISO 27001 certified?
Most UK organisations take between six and twelve months to achieve full certification. This timeline depends on the complexity of your operations and the results of your initial gap analysis. Small businesses with simple IT setups might move faster, while larger enterprises require more time for documentation and staff training. It’s vital to allow enough time for the “evidence of practice” phase before your official Stage 2 audit begins.
Can a small business achieve ISO 27001 compliance?
Is ISO 27001 a legal requirement in the UK?
ISO 27001 is the main standard that contains the requirements for your management system and is the only one you can be certified against. ISO 27002 is a supporting document that provides detailed guidance on how to implement the 93 controls found in Annex A. Think of 27001 as the “what” you must achieve and 27002 as the “how” you actually put those security measures into practice across your company.
Does ISO 27001 cover UK GDPR requirements?
It covers many aspects but not everything. ISO 27001 is excellent for meeting the “security of processing” requirements under UK GDPR, but it doesn’t specifically address data subject rights or lawful bases for processing. We recommend using the standard as a robust technical foundation for your privacy strategy. It ensures your data is protected, which makes meeting your broader legal obligations under the Data (Use and Access) Act 2025 much simpler.
What happens if we fail an ISO 27001 audit?
Failing an audit usually means the auditor has found “non-conformities.” Major non-conformities mean your certification is paused until you fix the issue and undergo a follow-up visit. Minor non-conformities won’t stop you from getting certified, provided you create a clear plan to address them before the next surveillance visit. It’s a collaborative process designed to improve your systems, and we’re here to help you remediate any technical gaps found during the audit.
How often do we need to renew our ISO 27001 certification?
Your certificate is valid for three years, but you must undergo annual surveillance audits to keep it active. These smaller audits ensure your organisation is still following its policies and adapting to new threats. At the end of the three-year cycle, you’ll complete a full recertification audit. This cycle encourages continuous improvement, ensuring that iso 27001 compliance for uk businesses remains a living part of your organisation’s culture and provides the long-term resilience your clients expect.
Posted on: June 15th, 2026 by Cornerstone
With the October 2025 transition deadline now behind us, any UK business still relying on the old 2013 standard is officially operating without a valid certificate. It’s a high-stakes reality that can stall commercial bids and leave your digital infrastructure vulnerable to modern threats. Achieving true ISO 27001 certification readiness in 2026 requires more than just a checkbox exercise. It demands a proactive shift toward the 2022 standard updates and the latest UK Data (Use and Access) Act requirements that came into force this February.
As a team recognized for our commitment to regional business excellence, we know it’s a challenge to document every process while keeping your daily operations running smoothly. It’s natural to feel some audit anxiety when you’re balancing growth with complex security controls. This guide is here to replace that uncertainty with a clear, strategic roadmap. You’ll discover how to benchmark your current security, close compliance gaps, and build a robust defense that protects your reputation. We’ve simplified the technical hurdles so you can achieve your goals with total confidence, treating your information security as the vital foundation of your business stability.
Key Takeaways
- Distinguish between identifying missing controls and verifying their performance through a formal readiness assessment before your audit begins.
- See how modern cloud solutions and Microsoft 365 configurations serve as the technical backbone for your compliance framework.
- Follow our five-step checklist to achieve ISO 27001 certification readiness while maintaining focus on your core business goals.
- Leverage the expertise of a local IT partner to automate evidence collection and handle the heavy lifting of digital security management.
- Build a culture where information security is a commercial advantage rather than just a technical necessity.
What is ISO 27001 Certification Readiness?
At its core, ISO 27001 certification readiness is the specific point where your Information Security Management System (ISMS) is fully documented, properly implemented, and supported by concrete evidence. It serves as the vital “pre-flight check” before you invite an external auditor for your formal Stage 1 and Stage 2 assessments. For businesses across the UK, achieving this state means you’ve moved past the planning phase and into a cycle of continuous improvement. This level of preparation is a significant commercial asset. It signals to your stakeholders and supply chain partners that you treat their data with the highest level of care. As your local expert, we believe this readiness creates the emotional security every business owner needs to grow with confidence.
The Shift to ISO/IEC 27001:2022
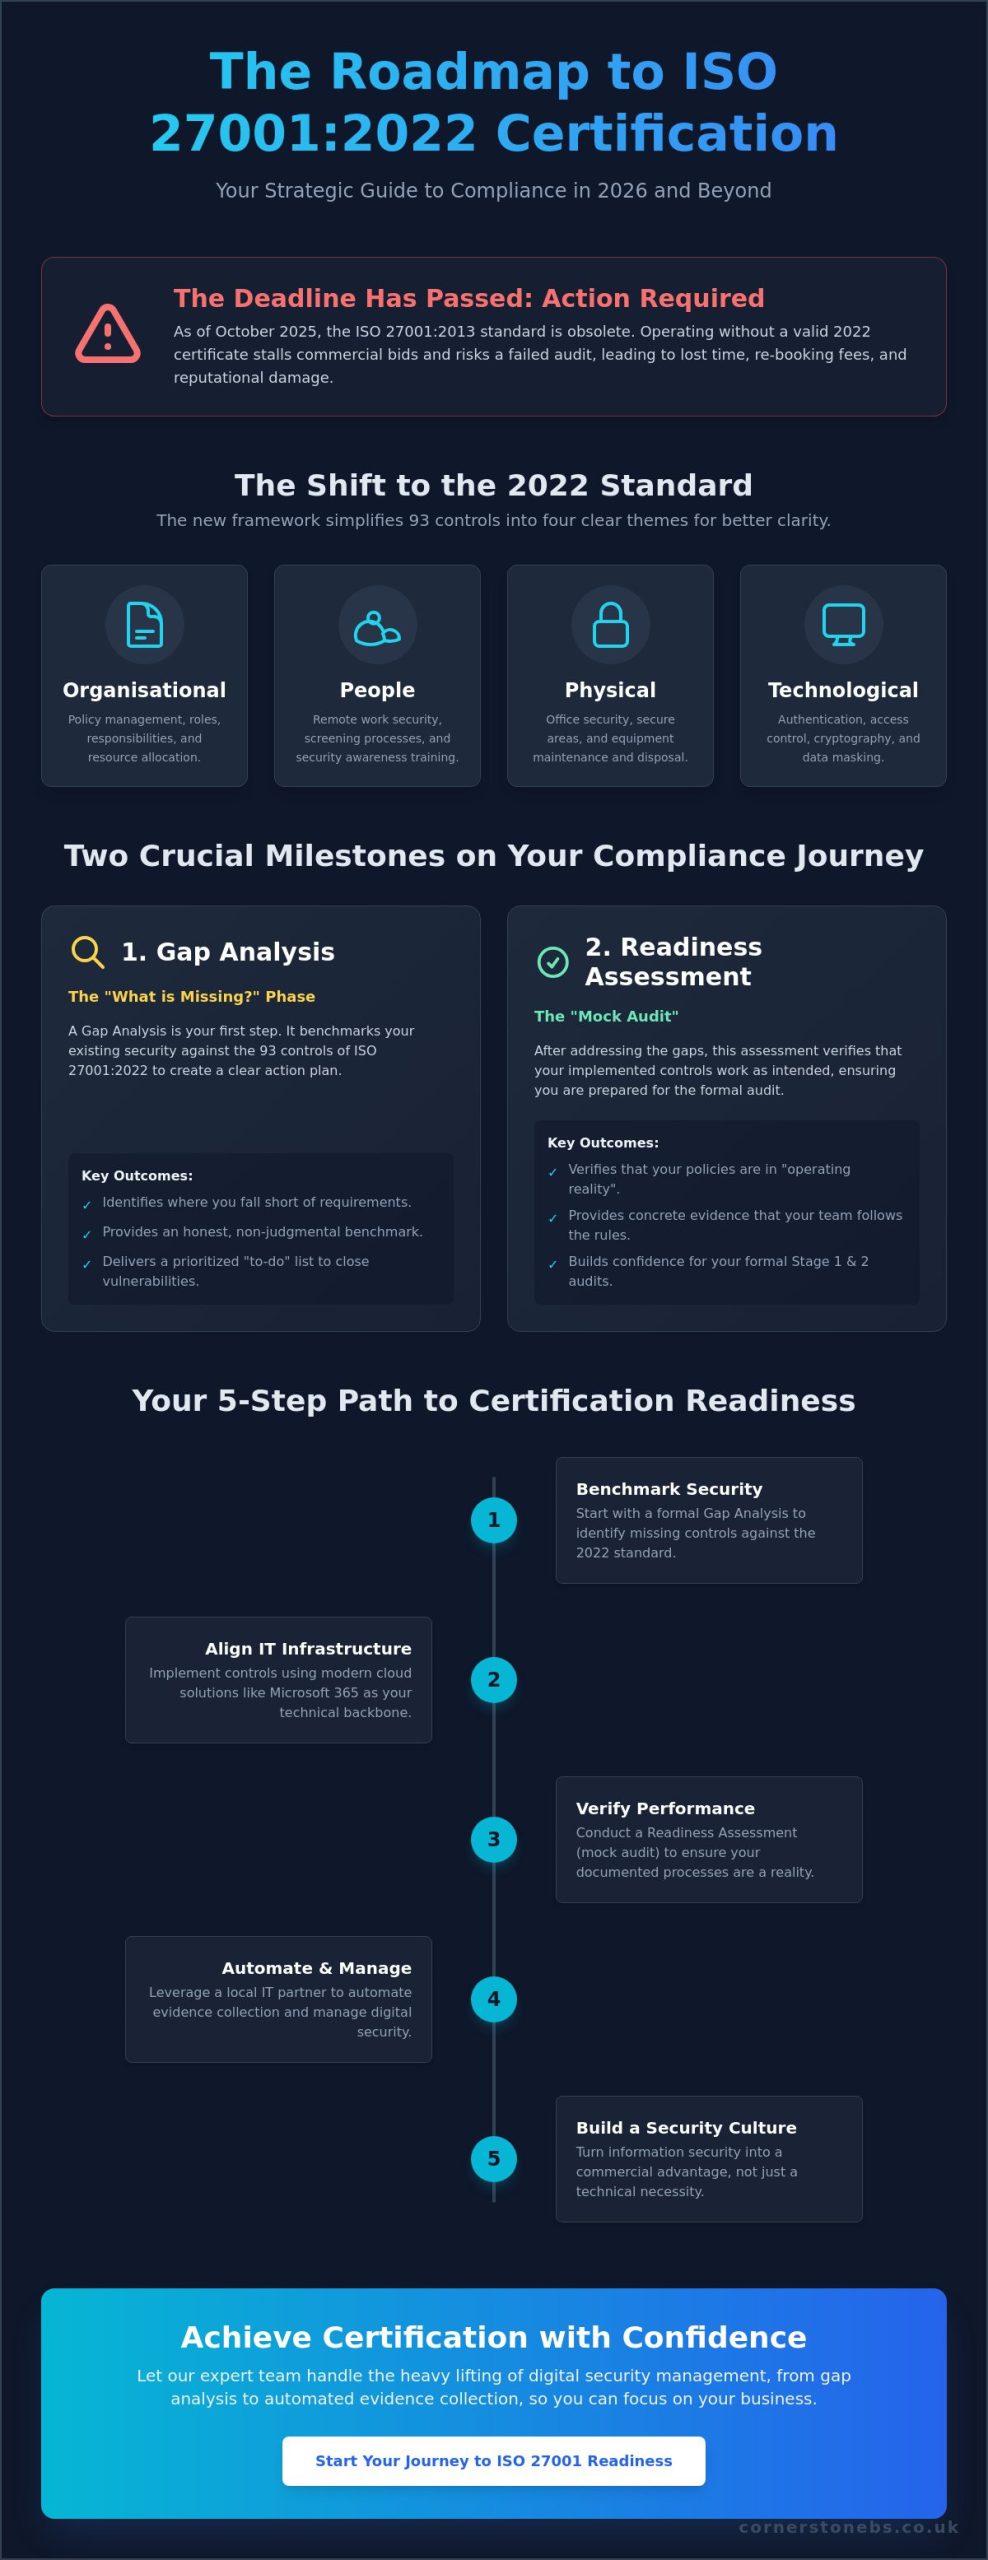
The recent shift to the ISO/IEC 27001:2022 standard changed the landscape for everyone. Since the transition deadline passed in October 2025, the old 2013 framework is no longer valid for new certifications. The 2022 update simplified the process by grouping 93 controls into four clear themes:
- Organisational controls like policy management and resource allocation.
- People controls such as remote working security and screening.
- Physical controls covering office security and equipment maintenance.
- Technological controls including authentication and data masking.
This structure makes it easier for business owners to understand where their responsibilities lie. Many firms fall into the trap of “false confidence,” assuming their old security habits will pass the new test. In reality, the 2022 standard requires a more integrated approach to modern digital risks and updated regulations like the Data (Use and Access) Act 2025. Modern readiness ensures your controls reflect the actual threats your business faces today.
Why Readiness Matters More Than Effort
Auditors are looking for “operating reality.” They want to see that your policies aren’t just sitting in a digital drawer. They’ll look for evidence that your team actually follows the rules you’ve set. If your documentation says you perform weekly backups, but you only have evidence for three out of the last four weeks, you’ll likely face a non-conformity. The cost of a failed audit goes far beyond the initial fee. You have to consider the time lost, potential re-booking charges, and the damage to your commercial reputation if a major contract is pending.
By focusing on ISO 27001 certification readiness, you turn your cyber security services into a permanent shield for your business. It ensures that when the auditor arrives, you can demonstrate your compliance with total ease. We view this as a foundational element of your stability, giving you the freedom to focus on your daily operations while we help manage the technical weight of compliance.
Readiness Assessment vs. Gap Analysis: Key Differences
Don’t mistake a gap analysis for a readiness assessment. While they share some DNA, they serve entirely different purposes on your journey toward compliance. We view these as distinct milestones in a bespoke technology roadmap, each designed to build your confidence and protect your investment. You can’t have a successful readiness assessment without first completing a thorough gap analysis; one identifies the work required, while the other verifies that the work actually functions as intended.
The Gap Analysis: Identifying the Holes
Think of the gap analysis as the “what is missing” phase. During this stage, we benchmark your existing security controls against the 93 controls defined in the official ISO 27001 standard. This isn’t about passing or failing; it’s about honest benchmarking. We look at your current digital infrastructure and identify where you fall short of the 2022 requirements.
The primary outcome of this phase is a prioritised “to-do” list for your IT team or managed partner. By using a formal risk assessment, we help you determine which gaps pose the greatest threat to your business continuity. This ensures you aren’t wasting resources on minor issues while major vulnerabilities remain open. If you’re feeling unsure about where to start, our local expert team is always available for an informal conversation to help you map out these initial steps.
The Readiness Assessment: The Mock Audit
Once you’ve implemented the necessary controls and policies, you move to the ISO 27001 certification readiness assessment. This is the “is it working” phase. We treat this as a full dress rehearsal conducted by an impartial expert who mimics the behaviour of a formal UKAS auditor. The focus shifts from “do you have a policy?” to “can you prove it’s working?”
During this mock audit, the expert will scrutinise your evidence, including:
- System logs and automated monitoring reports.
- Meeting minutes that show leadership engagement with security.
- Staff interviews to ensure your team understands their security responsibilities.
- Documented evidence of recent risk treatments.
This phase concludes with an Executive Briefing. This report gives you the green light to proceed or highlights specific areas that need one final polish. It’s the ultimate safety net that ensures you don’t pull the trigger on a formal audit until you’re absolutely certain of a positive outcome. This structured approach minimises disruption to your daily operations and keeps your certification journey on a steady, predictable path.
Aligning Your IT Infrastructure with 2026 Standards
Your digital foundation determines how smoothly you’ll reach the finish line. In 2026, a secure infrastructure isn’t just about speed; it’s about granular control and visibility. For most UK businesses, this starts with securing cloud solutions like Azure and AWS. These platforms offer incredible flexibility, yet they require expert configuration to ensure that data residency and access permissions align with your Information Security Management System (ISMS). When your infrastructure is built correctly, it acts as a silent partner in your ISO 27001 certification readiness journey.
A successful Microsoft 365 migration for business UK provides the perfect opportunity to bake security into your daily workflows. By moving away from legacy on-premise servers, you gain access to enterprise-grade tools that simplify the path to compliance. However, your chosen it company solutions must be designed to support these goals. If your technology stack is clunky or poorly integrated, your team will find workarounds that create security gaps and lead to audit failure. We’ve seen how a well-structured network provides the emotional security needed to scale without fear.
Securing the Microsoft 365 Ecosystem
Modern auditors love automation. Tools like Microsoft Intune and Purview allow you to automate the collection of evidence, proving that your devices are encrypted and your data is classified correctly. In a hybrid work environment, identity is the new perimeter. Protecting this perimeter requires Multi-Factor Authentication (MFA) and strict conditional access policies. Microsoft 365 Business Premium directly addresses at least five Annex A controls by managing access rights, securing authentication, protecting endpoint devices, automating information deletion, and restricting privileged access.
Network Infrastructure & Physical Security
The 5-Step ISO 27001 Readiness Checklist
Achieving ISO 27001 certification readiness doesn’t have to be an overwhelming ordeal. We’ve streamlined the process into five actionable steps that protect your time and your investment. By following this roadmap, you ensure that every part of your Information Security Management System (ISMS) is robust, compliant, and ready for the spotlight of a formal audit.
- Step 1: Define the Scope. Be precise about what you’re certifying. You don’t always need to include every department; focus on the areas that handle sensitive data or critical business processes.
- Step 2: Leadership & ISMS Policy. Auditors look for the “tone from the top.” Your senior management must demonstrate a clear commitment to security through documented policies and resource allocation.
- Step 3: Risk Assessment & Treatment. Identify the threats to your information and decide how to handle them. You must document why you chose to accept, transfer, or mitigate specific risks.
- Step 4: The Statement of Applicability (SoA). This is your auditor’s map. It lists which controls apply to your business and, crucially, which ones don’t.
- Step 5: Internal Audit & Management Review. This is your final check. You must conduct an internal audit to verify that your controls are working and present the findings to your leadership team.
If you’re worried about the technical burden of these steps, our locally based team can help you navigate the complexities with multi-award-winning expertise.
Mastering the Statement of Applicability (SoA)
The SoA is the most critical document you’ll present to a Stage 1 auditor. It lists which of the 93 Annex A controls from the 2022 standard are relevant to your operations. You cannot simply exclude controls because they seem difficult; every exclusion requires a valid, documented reason that the auditor will scrutinise. A well-crafted SoA proves you understand your unique risk landscape and have intentionally chosen the right safeguards to protect your business stability.
Preparing Your People for the Audit
Information security is as much about people as it is about technology. Staff awareness is a major component of ISO 27001 certification readiness. During a formal audit, the assessor may interview your team to see if they understand your security policies. We recommend regular training sessions and mock social engineering tests, such as simulated phishing emails, to keep security top of mind. You must document this training and any subsequent competency checks. This evidence shows the auditor that security is woven into your company culture, providing the emotional security your clients expect from a professional partner.
How Managed IT Support Accelerates Your Path to Certification
Achieving ISO 27001 certification readiness is often viewed as a daunting technical mountain to climb. However, partnering with a multi-award-winning managed IT provider shifts that weight off your shoulders. We don’t just give you a list of things to do; we implement the technical controls, configure the secure environments, and manage the ongoing monitoring that auditors demand. This proactive approach ensures your security controls are always active and functional, rather than just existing as words in a policy document. We treat your security as a foundational element of your business stability.
In the current 2026 threat landscape, staying ahead of sophisticated cyberattacks is a full-time commitment. Our team understands the specific nuances of the UK’s latest regulations, including the Data (Use and Access) Act 2025. We provide the technical evidence your auditor needs, from automated log reports to proof of encryption across all endpoints. This collaboration turns a complex certification process into a structured, manageable journey. We act as your long-term partner, ensuring your security foundation is strong enough to support your most ambitious growth plans while protecting your commercial reputation.
From Project to ‘Business as Usual’
Many businesses treat certification as a one-off project, but it’s actually a three-year cycle. After your initial success, you’ll face annual surveillance audits to prove you’re still meeting the standard. Managed IT support turns compliance into a standard operating procedure rather than a yearly scramble. Through regular technical audits and rigorous patch management, we ensure your systems remain secure every single day. This consistency removes the audit panic that often strikes when a surveillance date approaches. We keep the evidence trail warm so your ISO 27001 certification readiness is a permanent state, not a temporary achievement.
The Cornerstone Approach to Security
We pride ourselves on being more than just a service provider. Our approach blends professional authority with an approachable, regional warmth that makes complex technology feel manageable for any business owner. We design bespoke solutions that fit your specific needs, providing the emotional security that comes from knowing your digital assets are protected by experts. As a locally based team, we’re deeply invested in the success of our community’s businesses and the stability of their infrastructure.
Your path to a more secure, reputable, and commercially competitive business starts with a simple step. We invite you to have an informal conversation with our friendly team of experts. Let’s discuss your certification goals and see how we can build a resilient future together. Whether you’re just starting your gap analysis or looking to polish your final readiness assessment, we’re here to help you move forward with total confidence.
Securing Your Commercial Future with Confidence
Transitioning to the 2022 standard is more than a regulatory hurdle; it’s a strategic opportunity to build a more resilient, trustworthy organisation. We’ve explored how a robust Statement of Applicability and a well-configured Microsoft 365 environment provide the concrete evidence auditors demand. By shifting from a “project” mindset to a “business as usual” approach, you ensure your ISO 27001 certification readiness remains a constant state of excellence. This proactive stance protects your commercial edge and builds lasting trust with your stakeholders.
As a multi-award-winning IT services provider and certified partner for Microsoft, IBM, and Cisco, we provide the technical depth and national UK coverage needed to secure your infrastructure. We believe in a partner-led approach that prioritises your emotional security and business stability. You don’t have to navigate these complex global standards alone. Our team is here to simplify the technical mechanisms so you can focus on what you do best.
Book a consultation with our award-winning security experts to assess your ISO 27001 readiness.
We look forward to helping you turn compliance into a powerful engine for your long-term growth and success.
Frequently Asked Questions
How long does it take to achieve ISO 27001 certification readiness?
Most UK small and medium enterprises take between 6 and 12 months to reach full ISO 27001 certification readiness. The exact timeline depends on your current security maturity and the resources you can dedicate to the project. If you already have robust digital infrastructure in place, you might find the process moves much faster. We always recommend a steady pace to ensure your team truly adopts the new security culture.
Is ISO 27001 a legal requirement for UK businesses in 2026?
ISO 27001 isn’t a universal legal mandate, but it’s increasingly a commercial necessity for UK businesses. While the law doesn’t force you to certify, many public sector contracts and large corporate supply chains now require it. It also serves as powerful evidence that you’re meeting the “appropriate technical and organisational measures” required by the Data (Use and Access) Act 2025 and UK GDPR.
What is the difference between ISO 27001 and Cyber Essentials Plus?
Cyber Essentials Plus is a technical snapshot focused on five specific security areas, while ISO 27001 is a holistic management system. Think of Cyber Essentials as a vital baseline and ISO 27001 as the complete architecture for your business stability. The 2022 version of ISO 27001 manages 93 controls across people, physical, and digital domains, offering a much broader shield for your reputation.
How much does an ISO 27001 readiness assessment cost?
The cost of a readiness assessment depends on the size of your organisation and the complexity of your data processes. Larger firms with multiple sites or complex cloud environments will require more time for a thorough review. While audit day rates for UKAS accredited auditors have risen recently due to a shortage of qualified professionals, investing in a readiness assessment prevents the much higher costs of a failed formal audit.
Can a small business with under 10 employees get ISO 27001 certified?
Absolutely, businesses with fewer than 10 employees can and do achieve certification. The standard is designed to be scalable, meaning you only implement controls that are relevant to your specific risks. Small teams often reach ISO 27001 certification readiness faster than larger corporations because their communication lines are shorter and their internal structures are less complex.
What happens if we fail our ISO 27001 Stage 1 audit?
Failing a Stage 1 audit simply means you have some homework to do before the final assessment. Your auditor will provide a report detailing any non-conformities or areas where your documentation is thin. You’ll need to address these issues before you can proceed to Stage 2. It’s best to view this as a helpful safety net that prevents a more costly failure during the final certification stage.
Do we need to buy expensive software to manage our ISO 27001 compliance?
You don’t need to purchase dedicated compliance software to meet the standard. While automated platforms can be helpful, many successful businesses manage their compliance using their existing Microsoft 365 ecosystem. The key to ISO 27001 certification readiness is the quality of your processes and the evidence you produce, not the price tag of the software you use to track them.
How often do we need to renew our ISO 27001 certification?
Your ISO 27001 certificate follows a three-year cycle. Once you’re certified, you’ll undergo annual surveillance audits in years one and two to ensure your systems are still performing well. At the end of the third year, you’ll need a full recertification audit to maintain your status. This cycle ensures that your security remains a proactive, foundational element of your business rather than a one-off project.
Posted on: June 9th, 2026 by Cornerstone
Did you know that 80% of phishing attacks now use AI-generated content to trick your team? It’s a sobering reality in 2026, where a single accidental click can bypass even the most expensive firewall. You likely already know that your staff are your first line of defense, but without clear rules, they can also be your biggest vulnerability. That is why learning how to create a cyber security policy for employees isn’t just a checkbox for HR. It’s a vital move to protect your local business from a global $10.5 trillion crime wave.
We understand the pressure of trying to balance tight security with a productive, happy workplace. It’s easy to feel overwhelmed by complex regulations like NIS2 or the threat of $50,120 per day FTC penalties. You want to keep your data safe without making your team feel like they’re working in a digital fortress. This guide will show you how to build a robust, compliant, and practical policy that empowers your workforce instead of slowing them down. We will walk through the essential components of a 2026-ready policy, from AI acceptable use to zero trust basics, ensuring your business stays resilient and your team stays confident.
Key Takeaways
- Transform your team into a “Human Firewall” by establishing a clear, formal agreement that defines everyone’s role in your business security.
- Follow our step-by-step guide on how to create a cyber security policy for employees that secures your “crown jewel” data without disrupting daily workflows.
- Identify the essential components of a 2026-ready policy, including Acceptable Use rules and modern data classification tiers.
- Discover why Security Awareness Training is the secret to turning a static document into a proactive defensive culture.
- Learn how to bridge the gap between paper policies and technical reality using automated tools like MFA and managed cloud solutions.
What is an Employee Cyber Security Policy and Why is it Essential?
An employee cyber security policy is a formal agreement between your business and your staff. It outlines the ground rules for using company technology and handling sensitive data. Think of it as a Computer Security Policy tailored specifically for the people using your systems every day. While firewalls and antivirus software are vital, they can’t stop a staff member from handing over a password to a convincing AI-generated phishing email.
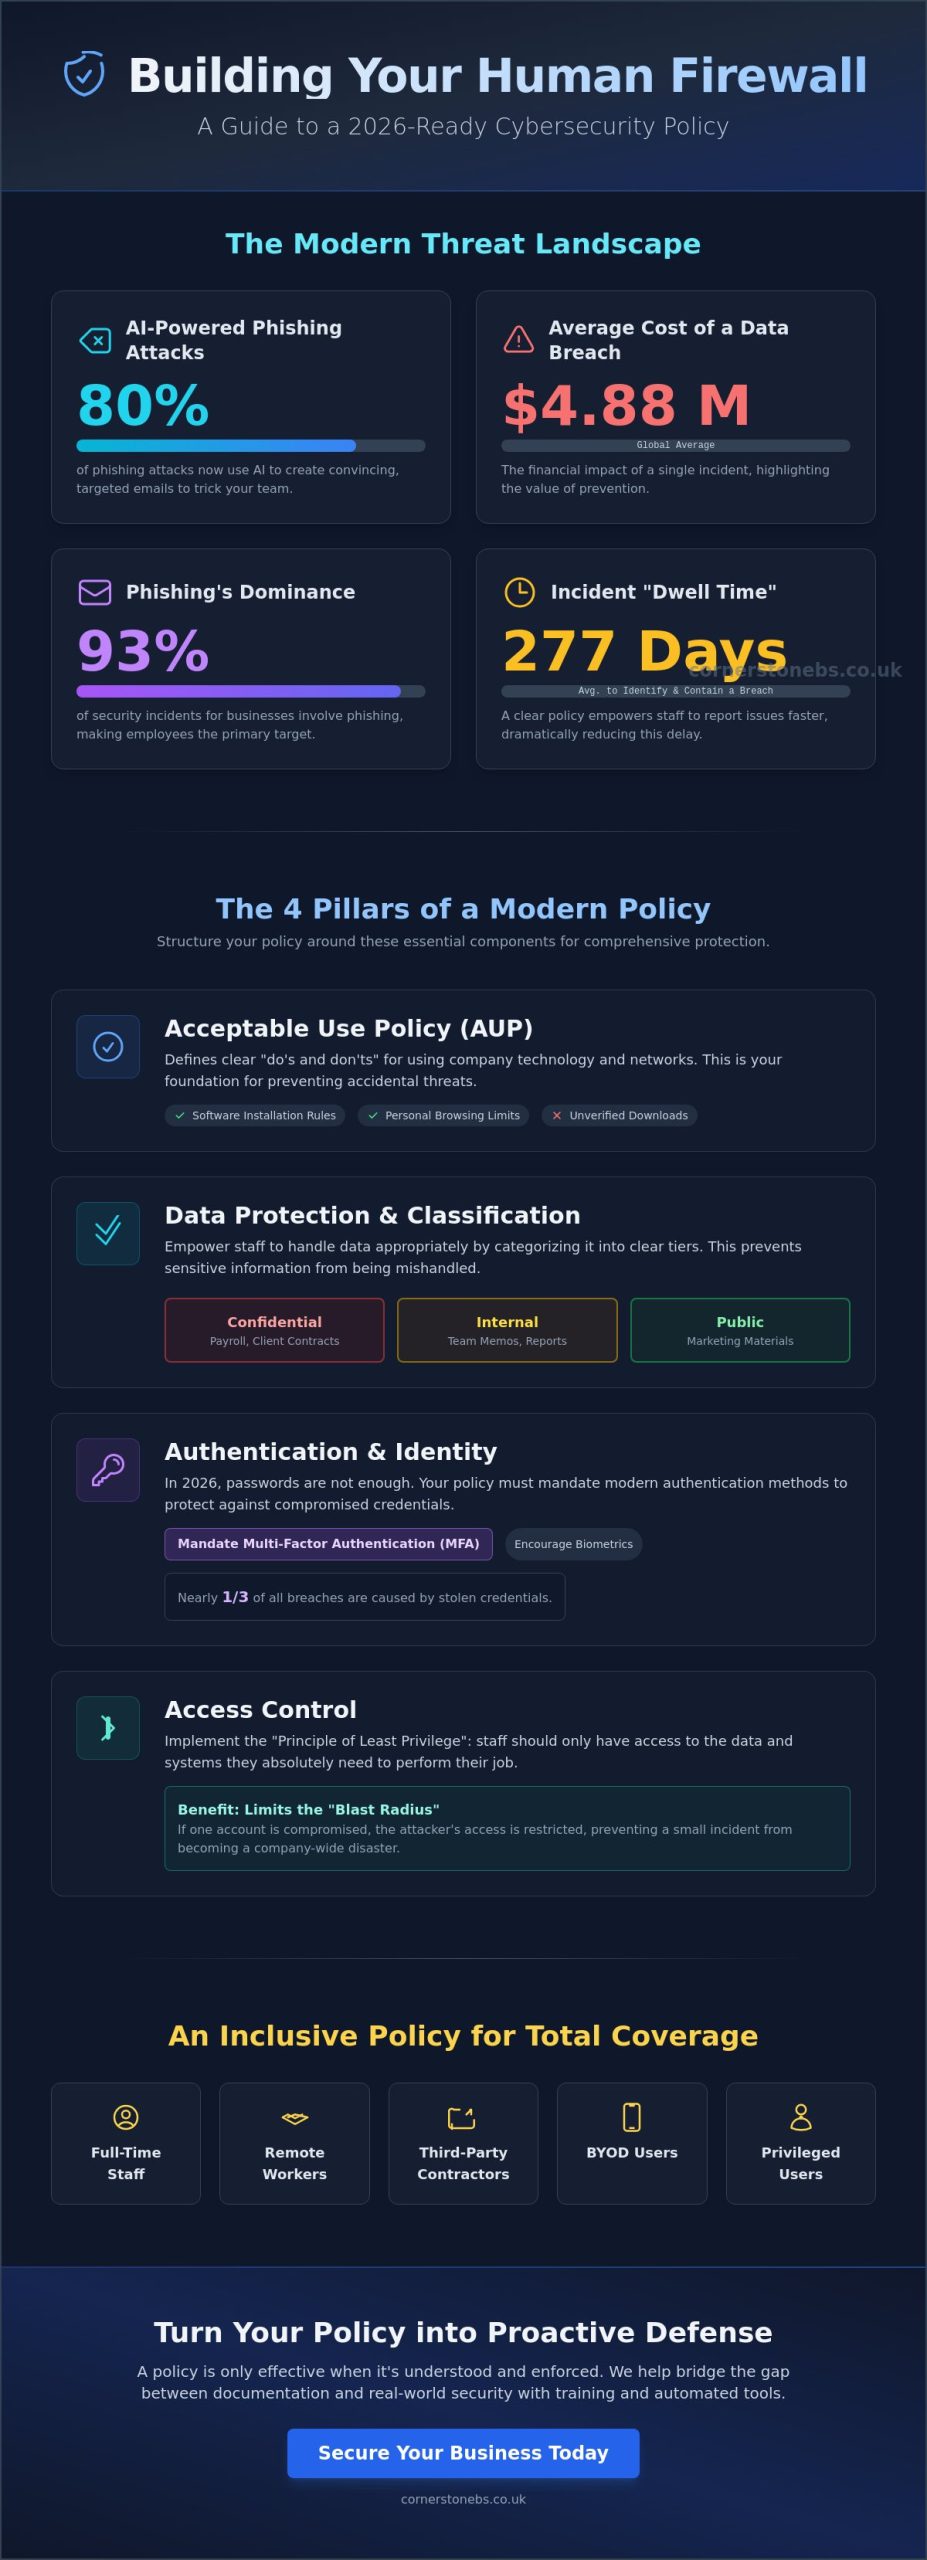
Building a “Human Firewall” is the goal. According to 2025 data, phishing is involved in 93% of incidents for businesses. This means your employees are your most frequent target. When you learn how to create a cyber security policy for employees, you’re giving your team the tools to spot these threats before they escalate. Prevention is always more cost-effective than recovery. The average cost of a data breach has now climbed to $4.88 million. For UK businesses, having this documentation isn’t just about safety; it’s about compliance. Standards like Cyber Essentials and GDPR expect you to have clear, written rules in place to protect personal data.
The Role of the Policy in Business Resilience
A solid policy does more than just prevent attacks; it helps you bounce back faster. On average, it takes organisations 277 days to identify and contain a security incident. Clear guidelines reduce this “dwell time” by teaching staff exactly how to spot and report suspicious activity. This proactive approach also makes your business more attractive to insurers. Many providers now require proof of formal cyber security services and policies before they will offer competitive premiums. It removes the panic from a crisis by providing a standard response protocol everyone can follow.
Who Should the Policy Cover?
Your policy must be inclusive to be effective. It should cover full-time staff, remote workers, and even third-party contractors who access your network. The “Bring Your Own Device” (BYOD) culture adds another layer of risk that needs specific rules. If an employee checks work emails on a personal phone, that device becomes a potential entry point for hackers. You also need to define “privileged users”. These are staff members with administrative access who carry extra responsibilities. Understanding how to create a cyber security policy for employees ensures every person connected to your business knows their specific role in keeping your data safe.
The Essential Components of a Modern Cyber Security Policy
A policy only works if it’s clear, actionable, and reflects the actual tech your team uses. When you look at how to create a cyber security policy for employees, start with an Acceptable Use Policy (AUP). This section defines exactly what is allowed on company systems. It covers everything from personal browsing habits to the software staff can install. By setting these boundaries early, you reduce the risk of accidental malware infections from unverified downloads.
Data protection is the next pillar. Your policy should categorise data into three tiers: public, internal, and confidential. Public data might be your marketing brochures, while confidential data includes payroll info or client contracts. Giving staff a clear framework helps them understand that a “confidential” document should never be stored on a personal cloud drive. If you’re feeling stuck on the structure, looking at official resources on how to create a cyber security policy can provide a solid baseline for these classifications.
Authentication is where many businesses fall short. In 2026, simple passwords aren’t enough. Your policy must mandate Multi-Factor Authentication (MFA) and encourage biometrics where possible. This is especially critical for email and communication. Since stolen credentials account for nearly one-third of all breaches, forcing an extra layer of identity verification is a simple way to stay resilient. We often help local firms implement these standards as part of our wider cyber security services to ensure the tech matches the talk.
Access Control and Identity Management
The “Principle of Least Privilege” is a vital concept here. It means staff only get access to the specific folders and apps they need to do their jobs. This limits the “blast radius” if an account is compromised. You also need a strict offboarding process. “Zombie accounts” from former employees are a huge security hole. Integrating these rules into your Microsoft 365 migration for business UK strategy ensures that permissions are managed centrally and securely from day one.
Addressing 2026 Threats: AI and Deepfakes
Your 2026 policy must address the rise of AI. With 80% of phishing attacks now using AI-generated content, staff need specific guidelines on using generative AI tools. They shouldn’t paste sensitive company data into public AI bots. Furthermore, establish a “double-check” protocol for urgent financial requests. If a “director” asks for a bank transfer via a video call or voice note, staff should verify this through a second, pre-approved channel to prevent deepfake fraud. Clear reporting mechanisms for these social engineering attempts will keep your team one step ahead of sophisticated hackers.
Step-by-Step: How to Create Your Cyber Security Policy
Creating a policy isn’t a one-size-fits-all job. It requires a deep dive into how your local team actually works. When you look at how to create a cyber security policy for employees, the process starts with listening, not just writing. A policy that looks good on paper but makes it impossible for your staff to do their jobs will simply be ignored. We want to build a framework that supports your growth while keeping the hackers at bay.
Phase 1: Discovery and Risk Assessment
Before you write a single word, you need to know what you are protecting. Start by auditing your current IT environment to identify your “crown jewel” data. This includes customer databases, financial records, and intellectual property. You must map out where this data lives, whether it is in the cloud, on-site servers, or accessed via mobile devices. A risk-first approach ensures you protect your most sensitive assets before worrying about low-impact vulnerabilities. Once you know where the risks are, you can map user roles to specific access requirements, ensuring no one has more power than they need.
Phase 2: Drafting for Clarity
The best policies are the ones people actually read. Avoid dense, academic language and “Thou Shalt Not” phrasing. Instead, use collaborative language that explains the “why” behind the rules. If employees understand that a rule exists to protect their own digital identity as well as the company, they are much more likely to follow it. Use “What to do if” scenarios to make the document actionable. For example, instead of a vague rule about phishing, provide a clear three-step process for what to do if a staff member clicks a suspicious link. Structure the document for quick reference so it serves as a helpful guide during a busy workday.
Once your draft is ready, don’t just hit “send” to the whole company. Consult with your department heads first. They will tell you if a new security measure, like a specific file-sharing restriction, will break a vital workflow. This consultation phase builds buy-in across the business. After adjusting for their feedback, review the document with your legal or IT partners. This ensures you meet UK standards like GDPR and Cyber Essentials. Finally, distribute the policy and collect signed acknowledgements. This isn’t just a formality; it’s a vital step in learning how to create a cyber security policy for employees that carries real weight and authority.
Implementation: Turning the Document into Defensive Action
Security Awareness Training (SAT) is the bridge that connects your written rules to real-world behaviour. It turns abstract guidelines into muscle memory. Since 80% of phishing attacks now use AI-generated content, your training must be as modern as the threats. Regular, bite-sized sessions keep security at the front of your team’s minds. This is not a one-off event. It is a continuous effort to ensure your staff remains your strongest defensive asset.
How you handle non-compliance dictates the success of your policy. If an employee clicks a suspicious link and fears for their job, they will likely hide the error. This silence gives hackers more time to move through your network. We advocate for a “no-blame” reporting culture. You want your team to speak up the moment they suspect a mistake. This transparency allows your IT team to contain threats before they become full-scale breaches. Discipline has its place for wilful negligence, but safety comes from open communication.
Building a Security-First Culture
Monitoring and Enforcement Tools
You cannot manage what you do not measure. Automated tools can flag policy violations in real-time, such as an employee attempting to access a restricted cloud folder. This provides an opportunity for “just-in-time” training rather than just a reprimand. Many businesses rely on managed IT services Teesside to monitor these systems around the clock. Regular phishing tests also help you see where your policy is working and where your team needs more support. Finally, set a firm schedule for annual reviews. Technology moves fast, and your policy must keep pace with new AI developments and regulatory changes.
If you want to see how your current setup compares to 2026 standards, chat with our local team for a straightforward review of your security posture.
How Cornerstone Business Solutions Enforces Your Policy
A policy is only as strong as the systems that back it up. While the previous sections focused on how to create a cyber security policy for employees, the real challenge lies in making those rules impossible to ignore. We help you move beyond paper security by embedding your policy directly into your digital infrastructure. This means your security isn’t just a suggestion; it is a technical reality that works in the background while your team stays productive.
Automation is the secret to consistent enforcement. We use robust cloud solutions to handle the heavy lifting, such as mandating MFA, enforcing regular password rotations, and ensuring data encryption is always active. When these processes are automated, you remove the risk of human error or forgetfulness. Your employees don’t have to remember to be secure; the system does it for them. This creates a seamless experience where protection and performance go hand in hand.
Even the best policy can’t predict every variable. That is why we provide 24/7 monitoring to catch the subtle anomalies that humans might miss. Whether it’s an unusual login attempt at 3 AM or an unexpected data transfer, our team is already on it. We also offer expert guidance to align your internal rules with global standards like Cyber Essentials and ISO 27001. This level of oversight gives you the confidence that your business is not just following a guide, but leading the way in regional security standards.
Bespoke Cyber Security Audits
Every business has unique habits and workflows. We start by identifying the specific gaps between your current operations and your ideal security posture. Our bespoke audits look at how your data actually moves, allowing us to tailor technical controls that match your specific needs. This transition from reactive fixes to proactive it company solutions ensures your growth is never compromised by avoidable risks. We don’t believe in generic templates; we believe in custom-built resilience that respects your time.
Your Partner in Long-Term Resilience
Choosing a partner is about trust and local expertise. Our multi-award-winning team understands the specific challenges facing UK SMEs because we’re part of the same community. We don’t just set up a system and walk away. We provide a dedicated helpdesk where your employees can get fast, friendly answers to their security questions. This ongoing support reinforces your policy every single day, turning technical support into emotional security for your team. We’d love to help you take the next step. Invite us for a conversation about your cyber security strategy and see how we can turn your policy into a powerful business asset.
Build a Resilient Future for Your Business
A great policy is more than just a list of restrictions. It’s a strategic blueprint that protects your assets while giving your team the confidence to use technology safely. We’ve explored how to create a cyber security policy for employees that balances strict compliance with a practical, collaborative culture. By auditing your risks and automating your defences, you ensure that your business remains a difficult target for increasingly sophisticated AI-driven threats.
You don’t have to manage this journey alone. As a multi-award-winning IT provider and a trusted Microsoft, IBM, and Cisco Partner, we specialise in turning complex security needs into simple, effective solutions. Our proactive 24/7 system monitoring acts as a safety net, catching the risks that humans might miss. We’re here to act as your long-term partner, helping you stay ahead of the curve in an ever-changing digital world.
Take the proactive step today to safeguard your hard work. Secure Your Business with an Expert Cyber Audit. Let’s have a conversation about how we can empower your workforce and protect your growth for years to come.
Frequently Asked Questions
Is a cyber security policy a legal requirement for UK businesses?
While there isn’t a single law titled the “Cyber Security Policy Act,” having one is practically mandatory for legal compliance. GDPR requires you to demonstrate how you protect personal data through “technical and organisational measures.” A written policy is the primary evidence of those measures. If you’re aiming for Cyber Essentials certification or working within regulated sectors, a formal policy is a non-negotiable requirement for your business.
How often should we update our employee cyber security policy?
You should review and update your policy at least once every twelve months. However, 2026 has shown that technology moves faster than the calendar. If you adopt new generative AI tools or undergo a major cloud migration, you need an immediate update. Keeping the document current ensures your team isn’t following outdated rules while facing sophisticated modern threats like deepfake fraud.
What is the difference between an Acceptable Use Policy and a Cyber Security Policy?
An Acceptable Use Policy (AUP) is a specific subset of your broader security strategy. It focuses on day-to-day staff behaviour, such as which websites are permitted and how company devices should be handled. A full cyber security policy is the wider umbrella. It covers high-level strategy, including data encryption standards, incident response protocols, and how you manage third-party vendor risks across your entire network.
Can I use a generic template for my company’s security policy?
Templates are a helpful starting point, but they shouldn’t be your final document. Every business has different “crown jewel” data and unique operational workflows. When you learn how to create a cyber security policy for employees, you’ll find that customisation is what actually drives protection. A generic document won’t address your specific network infrastructure or the unique risks your local team faces daily.
How do I get employees to actually read the security policy?
Ditch the dense jargon and keep your language punchy and direct. Long, academic documents are usually ignored or skimmed. We recommend using “What to do if” scenarios and regular, bite-sized training sessions to make the content stick. When employees understand the “why” behind a rule, such as protecting their own digital identity, they’re much more likely to engage with the material.
What should be the disciplinary action for a policy breach?
Disciplinary action should be fair, transparent, and tiered based on the severity of the breach. For honest mistakes, like a first-time phishing click, re-training is the most effective path. For repeated or wilful negligence, formal warnings may be necessary. The goal is to maintain a “no-blame” reporting culture where staff feel safe admitting to errors so your IT team can contain threats quickly.
Does a cyber security policy help with GDPR compliance?
Yes, it’s a foundational element of your GDPR strategy. The regulation expects organisations to prove they’ve taken proactive steps to secure personal data. A well-documented policy shows the Information Commissioner’s Office (ICO) that you’ve established clear rules for data handling and protection. It acts as a vital shield, potentially reducing fines if a breach occurs despite your best efforts.
Should remote workers have a different security policy?
Remote workers don’t need a completely different document, but they do need specific sections tailored to their environment. Your core policy should include clear rules for home Wi-Fi security, VPN usage, and the physical safety of company hardware in public spaces. Learning how to create a cyber security policy for employees that covers both the office and the home is essential for maintaining business resilience in 2026.