Posted on: August 29th, 2026 by Cornerstone
With 43% of UK businesses reporting a cyber breach in the last year, the old “castle and moat” security model has officially crumbled. If you feel overwhelmed by technical jargon or worry that your remote team is a walking security risk, you aren’t alone. Most small business owners feel caught between rising threats and tight budgets. We understand that your priority is growth, not deciphering complex code. That’s why zero trust implementation for smbs is no longer a luxury reserved for tech giants; it’s the foundation of a resilient, modern business in 2026.
We agree that security should feel like a supportive partner, not a confusing hurdle. You deserve the peace of mind that comes from knowing your data is secure in a hybrid world, without needing an enterprise-sized bank account to achieve it. This guide strips away the complexity to show you exactly how to move beyond outdated passwords to a “never trust, always verify” model. We’ll walk through a realistic, jargon-free roadmap that aligns with the latest 2026 NCSC guidance and the Data (Use and Access) Act 2025. You’ll discover how to protect your team and your reputation with practical steps you can start taking today.
Key Takeaways
- Shift your security strategy from a “castle and moat” model to a “never trust, always verify” approach that secures data in a hybrid world.
- Discover how zero trust implementation for smbs prioritises identity verification and device health to block unauthorised access before it happens.
- Learn why modern Zero Trust Network Access (ZTNA) offers better protection than traditional VPNs by providing granular access to specific applications.
- Follow a clear 5-step roadmap to audit your current permissions and implement mandatory multi-factor authentication across all cloud services.
- Understand the value of a long-term partnership with a managed IT provider to ensure your security infrastructure is proactive and resilient.
What is Zero Trust Security and Why Does It Matter for SMBs?
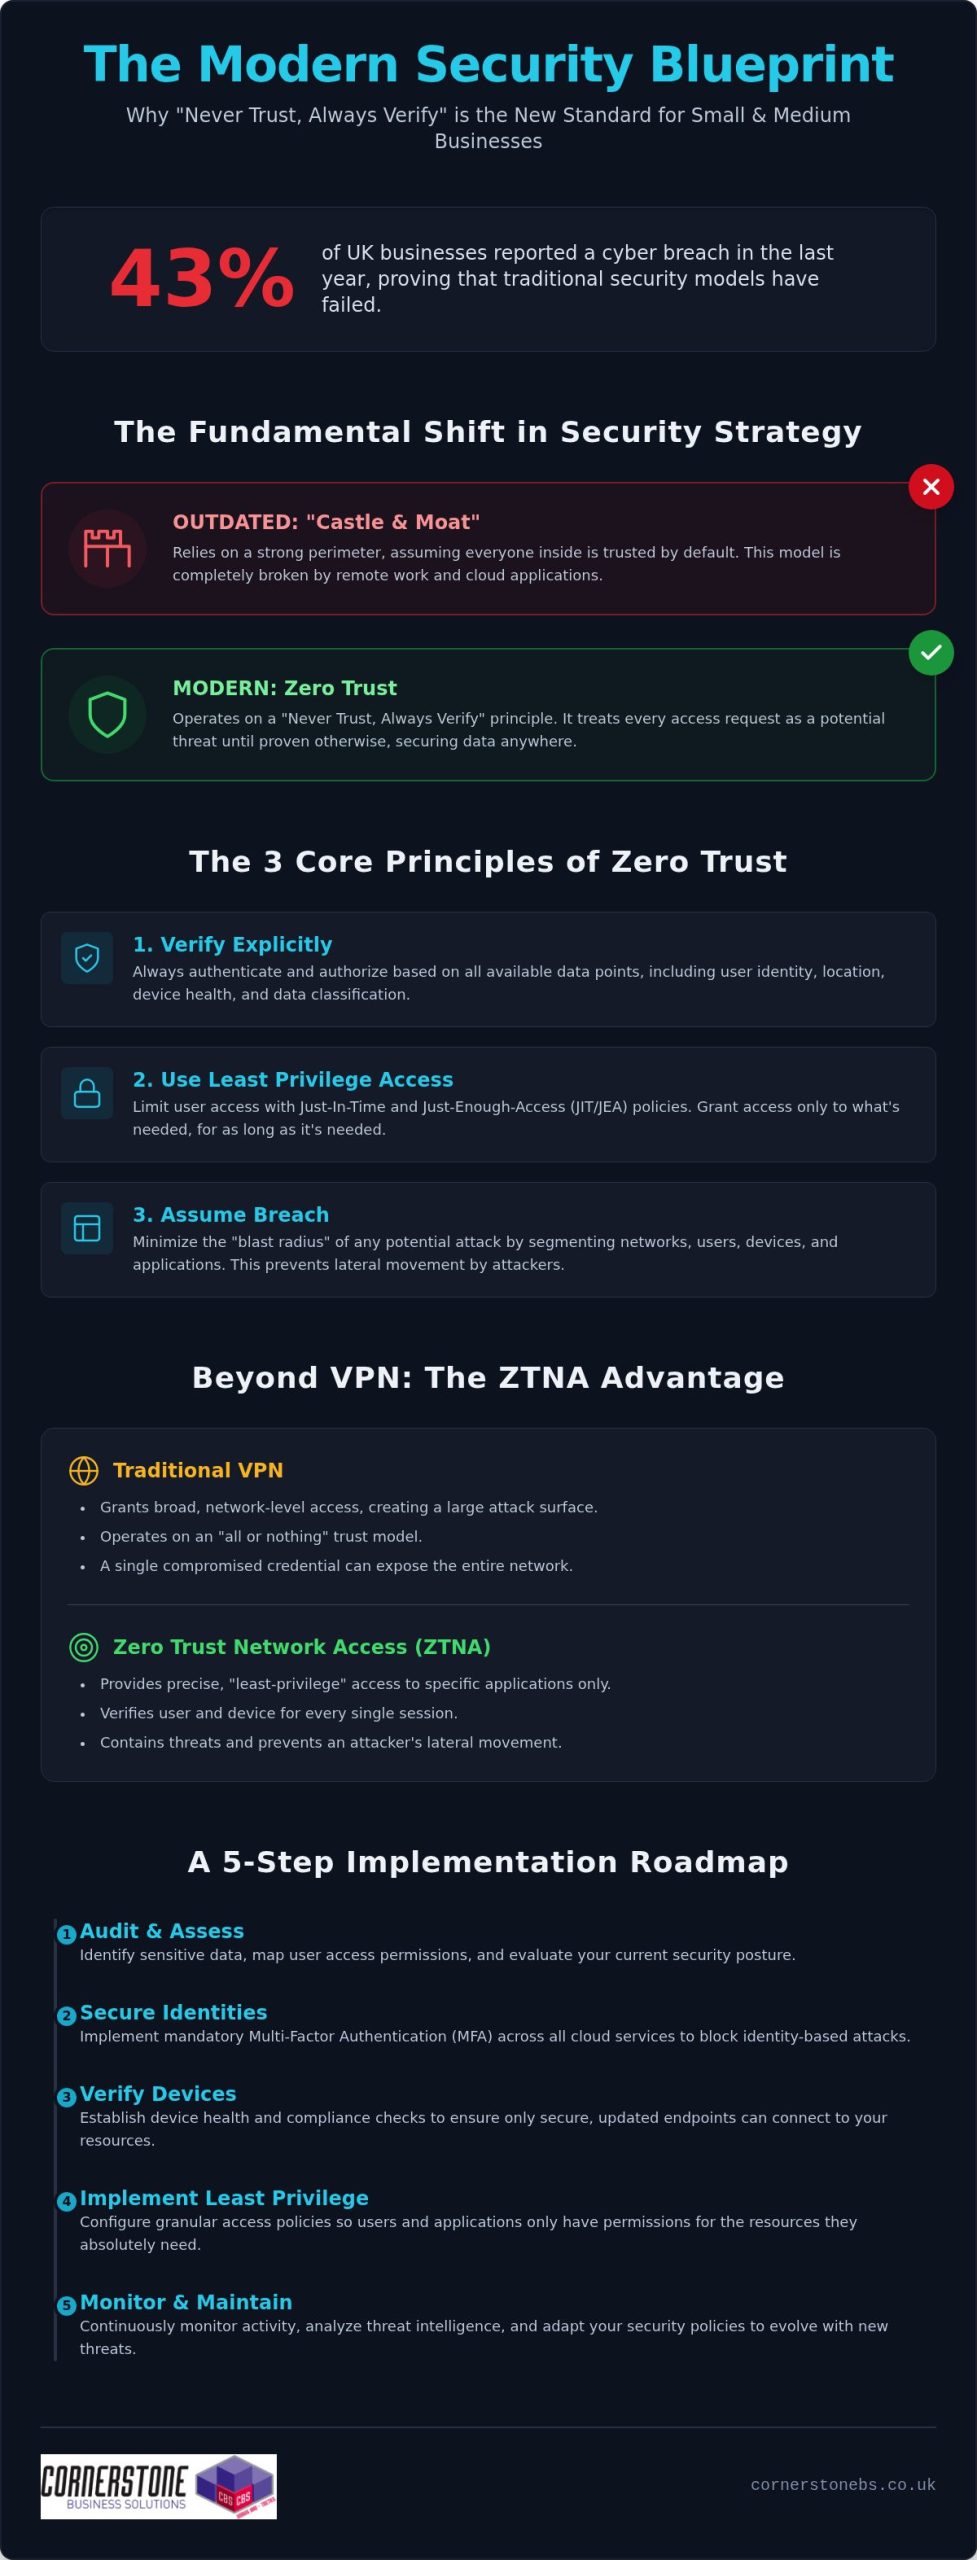
Zero Trust isn’t just a technical upgrade. It’s a fundamental shift in how we protect your hard-earned business. For decades, the “Castle and Moat” model was the standard. You built a strong perimeter around your office and assumed everyone inside was safe. But in 2026, that wall has effectively disappeared. With teams working from home and data living in the cloud, there is no longer a single “inside” to protect. A Zero Trust Architecture operates on a simple, powerful rule: never trust, always verify. Every request for access is treated as a potential threat until the system proves otherwise.
We help our partners adopt an “Assume Breach” mindset. This isn’t about being pessimistic. It’s about being proactive. By designing your systems as if a threat is already present, you stop a single compromised password from becoming a company-wide disaster. For UK small businesses, zero trust implementation for smbs is the most effective way to protect your reputation and ensure long-term financial stability. It provides the peace of mind you need to focus on growth while we handle the digital heavy lifting.
The Three Core Principles of Zero Trust
To build a resilient business, we follow three non-negotiable rules. First, we verify explicitly. This means authenticating every user based on their identity, location, and device health every time they log in. Second, we apply least privilege access. We ensure your staff only have access to the specific data they need for their roles. This uses Just-In-Time and Just-Enough-Access (JIT/JEA) protocols to keep your most sensitive files locked away. Finally, we assume breach. We segment your network to minimise the “blast radius” of any potential attack, ensuring your core operations stay stable even during an incident.
Why Traditional Security is No Longer Enough
The old ways of working simply don’t match the modern threat environment. Sophisticated phishing and ransomware attacks now target UK small businesses with alarming precision. As you moved your operations to Microsoft 365 and other cloud platforms, the traditional security perimeter broke. Your data is now accessed from various devices and locations, making the “insider threat” a very real concern. Identity has become the new security boundary. Relying on a basic VPN or a single firewall leaves you vulnerable. If a hacker steals one set of credentials, they can often roam freely across your entire network. Zero Trust stops this movement in its tracks, keeping your data where it belongs.
The Core Pillars of a Zero Trust Implementation
A successful zero trust implementation for smbs relies on four foundational pillars: identity, devices, applications, and data. These elements must work in harmony to create a seamless security blanket around your organisation. While the technical details are complex, the goal is simple. We want to ensure that only the right people, using the right devices, can access your sensitive information at the right time. This framework aligns with the global standards defined in NIST Special Publication 800-207, which serves as the definitive guide for modern digital defences.
- Identity: Every login attempt is a moment of truth. We use Multi-Factor Authentication (MFA) and biometrics to verify that your staff are who they say they are, every single time.
- Devices: We check the “health” of every laptop, tablet, and phone. If a device is missing a critical update or lacks encryption, it doesn’t get in.
- Applications: Whether you use cloud tools like Microsoft 365 and Xero or older on-premise software, access is granted on a per-app basis rather than giving away the keys to the whole network.
Identity as the New Perimeter
Passwords are no longer enough to keep your business safe in 2026. We move your team toward robust Multi-Factor Authentication (MFA) to block the vast majority of identity-based attacks. The real intelligence happens with Conditional Access policies. These “if, then” rules act as a smart filter for your business. For example, if a staff member tries to log in from an unrecognised location on an unmanaged device, the system can automatically block access or demand extra biometrics. Identity Protection is the gatekeeper of the modern business. By securing the user, we secure the primary entry point to your entire operation.
Securing the “Anywhere” Workforce with Endpoint Management
The rise of hybrid work has made unmanaged personal devices (BYOD) a significant risk for UK small businesses. If an employee’s personal tablet is infected with malware, it could easily spread to your company files the moment they log in. We solve this by using professional endpoint management tools like Microsoft Intune. This allows us to set and enforce strict security standards for any device touching your data. We automate updates and patches, closing the door on known vulnerabilities before hackers can exploit them. This proactive approach ensures your team can work from anywhere with total confidence. If you’re concerned about your current device security, our team can provide a clear cyber security review to help you identify any hidden gaps.
Zero Trust vs. Traditional VPNs: Making the Switch
Most UK small businesses still rely on traditional VPNs to connect their remote teams in 2026. While these tunnels were once the standard, they now represent a significant security gap. The problem is that VPNs usually grant “flat” network access. Once a user verifies their identity at the gate, they can often roam across your entire server. If a single device is compromised, your whole firm is at risk. Moving to a more modern approach isn’t just a technical upgrade; it’s a vital step for your long-term stability.
The Problem with “Trust but Verify”
Traditional firewalls struggle in a world where your data lives in the cloud and your staff work from various locations. They rely on a “trust but verify” model that is too easily exploited. Hackers love VPNs because they allow for lateral movement. This means one stolen credential can lead to a full-scale ransomware attack. By following the NCSC’s Zero Trust Architecture design principles, we help you move toward a model built for business resilience and peace of mind. It’s about ensuring an incident on one laptop doesn’t bring down your entire operation.
Zero Trust Network Access (ZTNA) Explained
Zero Trust Network Access (ZTNA) is the modern alternative that provides granular control. Instead of connecting a user to your whole network, ZTNA creates a “segment of one” for every session. Your staff only see the specific applications they need to do their jobs. A major benefit is that ZTNA hides your applications from the public internet entirely. Attackers can’t hack what they can’t see. This makes a zero trust implementation for smbs much more effective than simply patching an old, vulnerable VPN.
Making the switch also improves your daily operations. ZTNA is typically faster and more reliable than clunky VPN clients that frequently drop out. Your team will enjoy a smoother experience, and you’ll save money by retiring expensive, high-maintenance hardware. We recommend a phased approach for businesses with existing infrastructure. You don’t have to rip and replace everything overnight. We can start by securing your most sensitive cloud apps first, then gradually move your legacy systems over. This steady transition ensures your business remains stable while your security grows stronger.
A 5-Step Zero Trust Implementation Roadmap for SMBs
Step 1: Identity Discovery. We start by auditing every user account and permission level. You’ll likely find old accounts or “permission creep” where staff have access they no longer need. We enforce Multi-Factor Authentication (MFA) across all cloud services immediately. This aligns with the 2026 Cyber Essentials requirement where MFA is now mandatory for all cloud users.
Step 2: Device Inventory. We identify every device touching your company data. By setting strict health standards, we ensure that only encrypted, patched, and managed devices can connect to your systems.
Step 3: Implement Least Privilege. We remove local admin rights from standard user accounts. This simple step stops 90% of malware from installing itself silently. We restrict access to sensitive folders so staff only see what they need to do their jobs.
Step 4: Network Micro-segmentation. We break your network into smaller, isolated zones. If a breach occurs in one area, it’s trapped. The rest of your business stays safe and operational.
Step 5: Continuous Monitoring. We use proactive system monitoring to spot unusual behaviour in real-time. If a user logs in from an unexpected location or starts downloading unusual amounts of data, our tools flag it instantly.
Starting with Microsoft 365 Business Premium
For most UK small businesses, Microsoft 365 Business Premium is the ultimate “Zero Trust starter pack.” It provides enterprise-grade tools like Defender for Business and Intune at a price point that makes sense for smaller firms. You don’t need to juggle a dozen different third-party security tools when everything is integrated into one platform. If you’re planning a Microsoft 365 Migration for Business UK, choosing this license is the smartest move you can make for your 2026 security roadmap.
Building a Security-Centric Culture
Technology is only half the battle. A zero trust implementation for smbs fails if your team doesn’t understand the “why” behind the new rules. We help you frame security as a collaborative effort rather than a set of chores. When staff understand that verifying their identity protects their own work and the company’s reputation, they become your strongest line of defence. We recommend short, jargon-free training sessions that focus on practical tips for staying safe in a hybrid world. If you’re ready to secure your future, our managed IT support team is ready to help you build a roadmap that fits your specific business needs.
The Cornerstone Approach: Your Partner in Zero Trust
Choosing the right partner for your zero trust implementation for smbs is the difference between a box-ticking exercise and true business resilience. At Cornerstone, we don’t just act as a transactional supplier. We position ourselves as a dedicated long-term partner, invested in the stability and growth of your organisation. Our multi-award-winning team brings the confidence of global partnerships with industry leaders like Microsoft, IBM, and Cisco directly to your doorstep. We combine this high-level expertise with the approachable, regional warmth you expect from a local team that understands your specific challenges.
We know that every business operates differently. A “one size fits all” security plan usually fits no one well. We tailor our Zero Trust roadmap to match your specific data flows, staff requirements, and growth plans for 2026. Whether you are managing a fully remote team or a hybrid office, we design a framework that protects your assets without slowing down your people. To ensure complete transparency, our professional service project fees provide clear, upfront costs for your implementation. You can explore our full range of Cyber Security Services to see how we build resilience into every layer of your organisation.
Ready to Secure Your Future?
Moving toward a “never trust, always verify” model is a journey, not a single event. Our award-winning team is here to guide you through every step with a reassuring and proactive attitude. We pride ourselves on being highly organised and technologically advanced, yet we remain friendly and reachable for every client we serve. We invite you to have an informal conversation with us about your current security posture. It’s a chance to simplify the complex and see how modern security can actually empower your business. If you’re ready to take the first step toward a more secure 2026, you can contact Cornerstone for a Cyber Security Audit today. Let’s work together to make your company data the most secure it has ever been.
Secure Your Business Resilience for 2026 and Beyond
Transitioning to a modern security model is about more than just technology; it’s about protecting your company’s hard-earned reputation and future. We’ve explored how replacing clunky, vulnerable VPNs with granular, identity-based verification streamlines your operations while keeping hackers at bay. A successful zero trust implementation for smbs is not a one-time project but a proactive partnership that evolves alongside your business growth.
As a multi-award-winning IT support provider and Microsoft Solutions Partner, we have the expertise to simplify this journey for you. You gain unlimited proactive helpdesk access and a local team dedicated to your long-term stability. It’s time to replace outdated security models with a robust framework built for the modern, hybrid world. Book Your Proactive Cyber Security Audit Today and let’s start a conversation about your long-term success. We’re here to help you lead with confidence and total peace of mind.
Frequently Asked Questions
Is Zero Trust too expensive for a small business?
Zero Trust is highly cost-effective when managed correctly. Most small businesses already own the necessary tools through their existing Microsoft 365 subscriptions. Instead of expensive hardware, we focus on smart configuration and proactive monitoring. This approach makes zero trust implementation for smbs a strategic investment in business continuity rather than a drain on your budget. It protects you from the massive costs of data breaches and downtime.
Will implementing Zero Trust slow down my employees?
Modern security should empower your team, not hinder them. Zero Trust Network Access (ZTNA) is typically much faster and more reliable than traditional, clunky VPNs that often drop out. Features like biometrics and single sign-on (SSO) allow your staff to access their tools securely with just a touch or a glance. We aim to create a seamless experience where security happens in the background, keeping your workforce productive and happy.
Do I need to replace all my hardware to start a Zero Trust journey?
You don’t need to rip and replace your existing IT hardware to begin. We use cloud-based management tools to check the health and security status of your current laptops and mobile devices. If a device meets your security standards, it gets in. If it needs an update, the system prompts the user to fix it first. This allows you to build a resilient architecture while respecting your current technology investments.
How does Zero Trust help with UK data protection compliance?
Zero Trust is a powerful tool for meeting the latest UK data protection standards. By enforcing granular access and continuous verification, you stay in line with the Data (Use and Access) Act 2025 and NCSC design principles. This model provides the detailed auditing and control that the Information Commissioner’s Office (ICO) expects from modern businesses. It gives you the confidence that your company data is handled with the highest level of care.
Can I implement Zero Trust if I still have an on-site server?
You can absolutely implement this model with a hybrid setup. We don’t require you to move everything to the cloud at once. We secure your on-site server by placing it behind a Zero Trust gateway. This ensures that even staff in the office must be verified before they can access sensitive folders. It’s a practical way to modernise your security while maintaining the legacy systems your business relies on every day.
What is the first step an SMB should take toward Zero Trust?
The first step is always an identity and access audit. We help you identify exactly who has access to your data and remove any unnecessary permissions. Enforcing Multi-Factor Authentication (MFA) across all your accounts is the single most effective action you can take right now. This foundation allows us to build a more complex zero trust implementation for smbs over time, ensuring your most vulnerable entry points are locked down immediately.
How does Zero Trust protect against ransomware?
Zero Trust stops ransomware in its tracks by blocking “lateral movement.” In a traditional network, once a hacker gets inside, they can move freely to encrypt all your files. With Zero Trust, we segment your network into isolated zones. Even if one laptop is compromised, the threat is trapped in a “segment of one.” This limits the damage and ensures your core business operations can continue without interruption.
Does Zero Trust replace my existing antivirus and firewall?
It doesn’t replace them; it makes them smarter. Traditional firewalls and antivirus tools are still useful, but they aren’t enough on their own in 2026. Zero Trust adds a vital layer of identity and device health verification that traditional tools simply don’t have. We integrate these elements into a single, proactive system that monitors your entire digital environment. This creates a much stronger, multi-layered defence than relying on old-fashioned perimeter security alone.
Posted on: August 25th, 2026 by Cornerstone
Ransomware prevention in 2026 is no longer about building a taller wall, but about creating a resilient ecosystem where identity is the new perimeter. With the UK recently named the most attacked country in Europe, the fear of business-ending downtime is a heavy weight for any leader to carry. You’re likely tired of complex jargon and skeptical of software that promises the world but delivers little. We understand you need a reliable ransomware prevention checklist that works for your specific team without the fluff.
This expert-led guide is designed to harden your business against modern threats like AI-enabled attacks and the growth of Ransomware-as-a-Service. We’ll show you how to move from reactive fixes to a proactive stance that aligns with the latest National Cyber Security Centre guidance and the new Cyber Security and Resilience Bill. By following these prioritized steps, you can ensure compliance with UK standards like Cyber Essentials and build the total resilience your company needs to thrive. It’s time to replace uncertainty with a clear, benefit-driven plan for your digital security and long-term peace of mind.
Key Takeaways
- Move beyond basic backups by learning how to defend against triple extortion tactics that threaten to leak your private data.
- Upgrade your technical hardening from traditional antivirus to proactive Endpoint Detection and Response for faster threat mitigation.
- Stop sophisticated credential theft by implementing phishing-resistant MFA that bypasses common hacker techniques like push notification fatigue.
- Use our expert-led ransomware prevention checklist to prioritize your security tasks and ensure full compliance with UK standards like Cyber Essentials.
- Explore how Managed IT Support offers a cost-effective way to maintain 24/7 monitoring and professional expertise for your digital infrastructure.
The Evolution of Ransomware in 2026: Why Basic Protection Fails
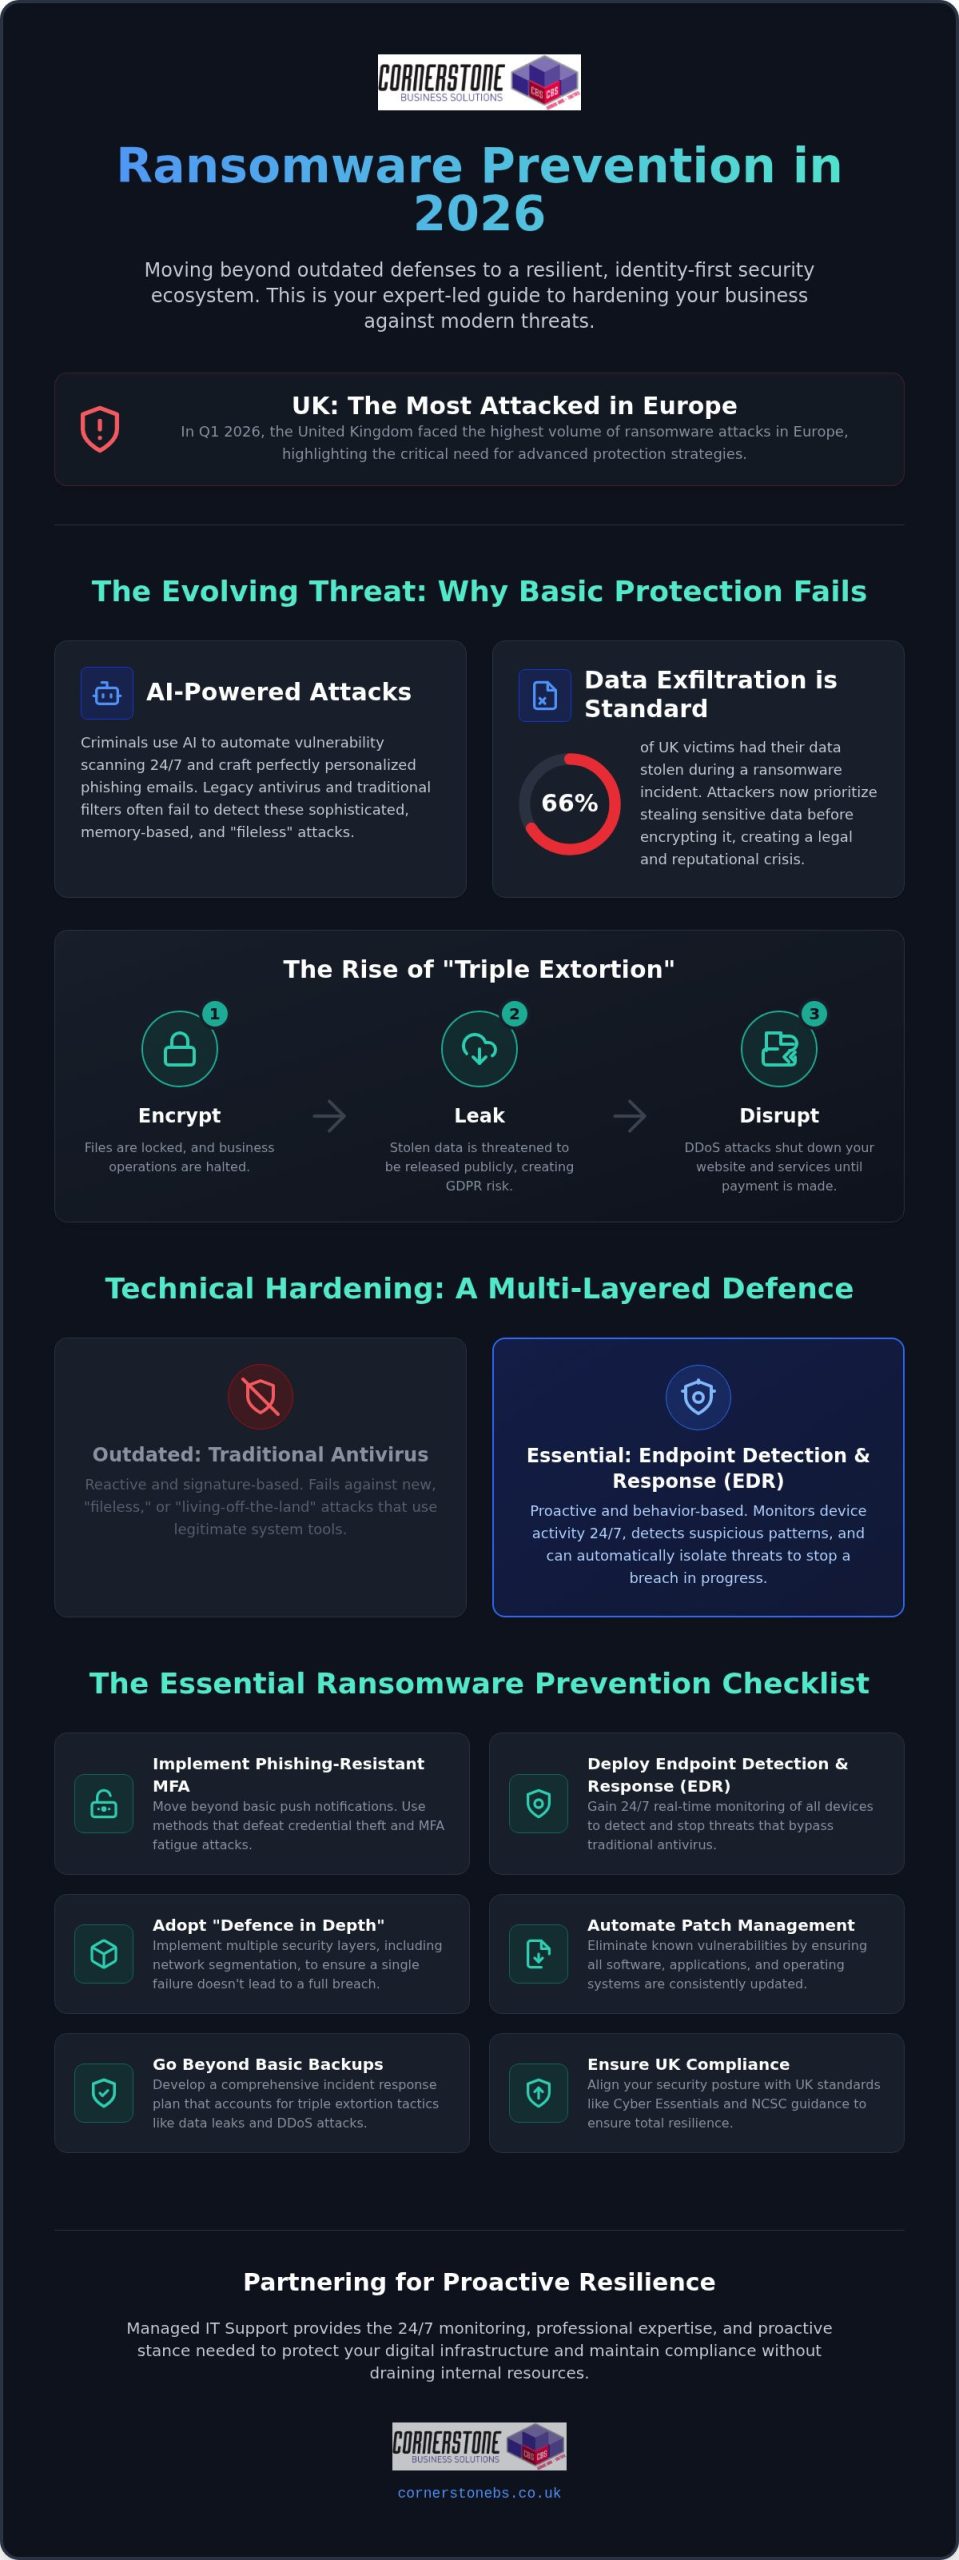
Ransomware has transformed from a simple nuisance into a sophisticated, multi-stage extortion event. In the first quarter of 2026, the United Kingdom became the most attacked country in Europe, proving that old-school defences are no longer enough. To understand why your current ransomware prevention checklist might be outdated, we need to look at how the threat has changed. Modern attacks aren’t just about locking files; they’re about total business leverage. If you’re still asking What is Ransomware?, the answer in 2026 is far more dangerous than it was even two years ago.
Hackers now use AI to automate the discovery of vulnerabilities, scanning your network for weaknesses 24/7. They don’t just wait for a lucky break; they create one. Legacy antivirus software often fails because it looks for known signatures or files. Today’s fileless malware attacks hide in your computer’s memory or use legitimate system tools to bypass detection entirely. We’re also seeing the rise of Triple Extortion. This is where criminals encrypt your data, steal it for public leak, and then launch a DDoS attack to shut your website down until you pay. It’s a relentless cycle that basic software can’t stop alone.
From Data Encryption to Data Exfiltration
Attackers have flipped the script. They now steal your sensitive data before they ever trigger the encryption process. This gives them a backup plan if your technical recovery is solid. Double Extortion is now the industry standard threat for 2026, where criminals demand payment specifically to stop the public release of your stolen information. For a UK business, this isn’t just a technical issue. It’s a legal nightmare involving massive GDPR fines and permanent damage to your brand’s reputation. According to 2026 data from Proofpoint, 66% of UK victims reported data theft during an incident, making it more likely than not that your data will be leaked if you’re hit.
AI-Driven Phishing and Social Engineering
The days of spotting a scam by its poor grammar are gone. Criminals now use Large Language Models (LLMs) to craft perfect, highly personalised phishing emails that look identical to a message from your bank or a trusted supplier. We’re also seeing a rise in Deepfake audio and video being used in business email compromise. A voice that sounds exactly like your director might call to authorize an urgent transfer. Traditional email filters struggle to catch this synthetic content because it lacks the usual red flags. This evolution makes identity security a foundational part of any modern ransomware prevention checklist.
Technical Hardening: Building a Multi-Layered Defence
Building a resilient business requires more than a single piece of software. It demands a strategy called “Defence in Depth.” This approach ensures that if one security layer fails, others are ready to catch the threat before it causes damage. A modern ransomware prevention checklist must move beyond basic firewalls to include integrated, intelligent systems that talk to each other. For a comprehensive look at these technical standards, the CISA #StopRansomware Guide provides a gold standard for configurations that every UK business leader should consider.
Automated patch management is another non-negotiable element. Hackers love unpatched software because it provides a predictable, open door into your network. In a hybrid work environment, your “perimeter” isn’t just the office walls. It’s every cloud application and remote device your team uses. Securing this cloud perimeter requires consistent updates and proactive monitoring to ensure your defences remain strong against evolving threats. Our team often finds that managed IT support is the most efficient way for businesses to maintain this level of technical hygiene without draining internal resources.
Endpoint Detection and Response (EDR)
Traditional antivirus is reactive. It waits to see a known file signature before it acts. EDR is different. It monitors the behaviour of every device on your network in real time. This is vital for stopping “Living off the Land” (LotL) attacks, where hackers use your own legitimate system tools to encrypt your data. Because most firms don’t have an in-house security team working through the night, managed EDR provides the constant oversight needed to stop a breach at 3 AM on a Sunday. It identifies suspicious patterns, like a sudden mass renaming of files, and isolates the device immediately.
Network Segmentation and Lateral Movement
Keeping your entire business on one “flat” network is a recipe for disaster. If a single laptop in your sales department gets infected, the hacker can move sideways across the network to your finance servers in minutes. Network segmentation acts like the bulkheads in a ship. By dividing your infrastructure into smaller, isolated zones, you can contain an infection to its source. This limits the “Blast Radius” of an attack, ensuring that a breach in one area doesn’t lead to total company downtime. It’s a core component of any effective ransomware prevention checklist in 2026.
Identity Security: Why MFA is No Longer a Silver Bullet
Many UK business owners believe that enabling basic Multi-Factor Authentication (MFA) makes them unhackable. It’s a common misconception. While MFA is a vital step in any ransomware prevention checklist, simple push notifications are now easily bypassed. Hackers use “MFA Fatigue” attacks, bombarding a tired employee with requests until they accidentally click “Approve.” By 2026, session hijacking and AI-powered credential theft have made traditional SMS or app-based codes insufficient.
We recommend moving toward Phishing-Resistant MFA, such as FIDO2-compliant hardware keys. These require a physical touch or biometric scan that can’t be intercepted by a remote attacker. This shift is a core recommendation in CISA’s #StopRansomware Guide, which emphasizes that identity is the new perimeter. If an attacker steals a password today, they shouldn’t automatically get the keys to your entire digital kingdom.
Implementing Zero Trust Architecture
Zero Trust isn’t a single software package you buy off the shelf. It’s a strategic mindset: “Never Trust, Always Verify.” This framework ensures that every user and device is checked every time they try to access your data, regardless of whether they are in the office or working from home. Our Cyber Security services help you build this resilience through three main pillars:
- Verify Explicitly: Always authenticate based on all available data points, including user identity, location, and device health.
- Use Least Privilege: Limit user access with “Just-In-Time” and “Just-Enough-Access” to only what they need for their specific role.
- Assume Breach: Design your systems as if an attacker is already inside the network to minimize the impact of a potential incident.
Cyber Awareness Training for the 2026 Workforce
Annual “tick-box” videos don’t stop modern attacks. Your team is your first line of defence, but they need training that reflects today’s AI-driven threats. We focus on creating a security-first culture where employees feel confident reporting a mistake rather than hiding it out of fear. Simulated phishing tests should now include deepfake audio scenarios and perfectly written AI emails. This ongoing education turns your staff into a human firewall, making your ransomware prevention checklist a living part of your daily operations.
The Essential Ransomware Prevention Checklist for 2026
Prevention is only half the battle. In 2026, true resilience means having the ability to survive and recover even if an attacker manages to breach your initial defences. This ransomware prevention checklist focuses on both stopping the entry and ensuring your business stays operational during a crisis. We believe that a proactive stance is the only way to protect your livelihood and your team’s hard work.
- Step 1: Conduct a comprehensive Cyber Security audit to find hidden gaps. This is the essential first step for any UK business to understand their current risk level.
- Step 2: Enforce Phishing-Resistant MFA across all business accounts to block sophisticated credential theft.
- Step 3: Implement the 3-2-1-1 Backup Strategy to ensure data is always recoverable.
- Step 4: Lock down Remote Desktop Protocol (RDP) and use secure VPNs for all remote access.
- Step 5: Establish a formal Incident Response Plan (IRP) and test it through monthly tabletop exercises.
If you aren’t sure where your business stands today, the best move is to book a professional security audit with our expert team to identify your most critical vulnerabilities.
The 3-2-1-1 Backup Strategy: Your Final Safety Net
In 2026, the traditional 3-2-1 rule is no longer enough because modern ransomware specifically targets and deletes backups. You need the extra “1” for immutability. Immutable backups are stored in a state that cannot be deleted, changed, or overwritten, even if a hacker gains administrative access to your network. Physically disconnected or air-gapped backups are the only true defence against encryption because they sit entirely outside the reach of the attacker’s software. You must also define your Recovery Time Objective (RTO) and Recovery Point Objective (RPO). RTO determines how quickly you need to be back online, while RPO defines how much data loss your business can actually tolerate before it becomes a disaster.
Patching and Vulnerability Management
Partnering for Resilience: Proactive Protection with Cornerstone
Trying to handle cyber security alone in 2026 is a high-risk strategy that often leaves UK firms vulnerable. Ransomware is no longer a simple virus; it’s a professional criminal operation. You need more than a static document to stay safe. You need a team that lives and breathes these threats every day. Our Managed IT Support provides the 24/7 monitoring and technical expertise required to turn your ransomware prevention checklist from a plan into a bulletproof defence.
We don’t just act as a reactive helpdesk. We position ourselves as your dedicated long-term partner, spotting the smoke before the fire starts. Proactive maintenance is always more cost-effective than emergency breach recovery. With financial losses from UK ransomware attacks increasing by 50% annually to approximately £270,000 per incident, the investment in professional oversight is a foundational element of your business stability and emotional security.
Why Outsourced Security Beats In-House Management
Managing a modern security stack requires expensive, enterprise-grade tools. Through our partnerships with industry leaders like Microsoft, Cisco, and IBM, we give you access to world-class technology without the massive upfront costs. There’s also a global talent shortage in cyber security. It’s difficult and expensive to hire a full in-house team that understands 2026-level threats. Our experts handle the complexity so you can focus on growth.
Our Cloud Solutions offer built-in resilience that traditional on-premise servers simply can’t match. We ensure your data is distributed and protected by the latest encryption standards. This allows your team to scale securely while we manage the technical infrastructure in the background. It’s a seamless way to tick off the most difficult items on your ransomware prevention checklist.
Building Your Disaster Recovery Plan
The first 60 minutes after discovering an attack are critical. Our rapid response process kicks in immediately to isolate the threat and protect your immutable backups. We focus on Business Continuity, ensuring you can keep working even if your primary systems are under pressure. We don’t just set up your systems and walk away; we test your recovery plans regularly to ensure they work when you need them most.
Following a checklist is a great start, but having a multi-award-winning team by your side provides the ultimate peace of mind. We’re proud to be a local team of experts who genuinely care about your success. We’d love to help you harden your defences and secure your future. Feel free to reach out for a no-obligation security conversation with our team today.
Building a Resilient Future for Your Business
Protecting your organization from modern threats requires more than just luck. We’ve seen how ransomware has evolved into a multi-stage extortion event where identity security and immutable backups are your strongest allies. By adopting a proactive stance and following a comprehensive ransomware prevention checklist, you replace fear with a clear strategy for growth. It’s about ensuring your team can work with confidence, knowing their data is secure.
As a multi-award-winning IT provider and official partner to Microsoft, IBM, and Cisco, we specialize in bespoke security solutions. Our UK-based proactive support desk acts as an extension of your team, providing the 24/7 oversight your business deserves. Don’t wait for a breach to discover your vulnerabilities. Book Your Comprehensive Cyber Security Audit with Cornerstone Today to harden your defences.
Taking these steps today secures your legacy for tomorrow. We’re ready to help you build a more stable, resilient business that’s prepared for whatever the digital world throws your way.
Frequently Asked Questions
What is the single most important step in ransomware prevention?
The single most important step is securing user identities through phishing-resistant Multi-Factor Authentication (MFA). Since most breaches begin with compromised credentials, hardware-based keys or biometrics create a barrier that software-only solutions can’t match. It’s the foundation of any modern ransomware prevention checklist. By ensuring that only verified users can access your network, you stop the majority of automated attacks before they can gain a foothold in your systems.
Should my business ever pay a ransomware demand in 2026?
Official guidance from the National Cyber Security Centre (NCSC) remains clear: you shouldn’t pay the ransom. Paying doesn’t guarantee your files will be returned and often funds further criminal activity. Under new UK legislation, organizations are also required to report incidents and consult with authorities within 72 hours. we focus on building resilience so that you don’t have to negotiate. A solid recovery plan is always a better investment than a ransom payment.
How often should we test our business backups?
You should perform full restoration tests at least once a quarter, though monthly testing is ideal for critical data. A backup is only as good as its last successful restore. Regular testing ensures your Recovery Time Objective (RTO) is realistic and that your team knows exactly what to do during an incident. This proactive approach identifies corruption or configuration errors early, giving you the peace of mind that your safety net is actually secure.
Does Microsoft 365 protect me from ransomware automatically?
Microsoft 365 offers strong foundational tools, but it doesn’t protect you from ransomware automatically without expert configuration. You must actively enable features like conditional access, advanced threat protection, and secure defaults to stop modern attacks. It’s a shared responsibility model where Microsoft secures the platform while you secure your data. Our team ensures your environment is hardened against the specific fileless malware and credential theft techniques that are prevalent in the UK today.
What is an immutable backup and why do I need one?
An immutable backup is a data copy that cannot be altered, encrypted, or deleted for a set period. Even if a hacker gains administrative privileges, they cannot destroy this data. In 2026, attackers specifically target backup servers to force a ransom payment. Having an immutable copy ensures you always have a “clean” version of your business data available for recovery, making the threat of permanent encryption much less significant for your operations.
How can I tell if my business has already been breached?
Look for subtle signs like unusual network latency, unexpected account lockouts, or unauthorized configuration changes. Modern attackers often stay “silent” in your network for weeks to exfiltrate data before triggering encryption. Implementing Endpoint Detection and Response (EDR) is the best way to spot these anomalies. EDR monitors behaviour in real time, alerting you to “Living off the Land” techniques that traditional antivirus software would likely miss until it’s too late.
Is Cyber Essentials certification enough to stop ransomware?
Cyber Essentials is an excellent baseline that covers approximately 80% of common cyber threats, but it isn’t a “set and forget” solution. It provides the foundational controls every UK business needs for compliance. However, to defend against the AI-driven and triple-extortion attacks of 2026, you need to layer this certification with advanced strategies like Zero Trust architecture and 24/7 proactive monitoring. It’s a vital part of your security journey, not the destination.
What is the cost of a ransomware attack for a UK SME?
Beyond the direct financial hit, the true cost of an attack in 2026 includes massive downtime and permanent reputational damage. Industry data from Sophos shows the average global recovery cost has risen to $1.7 million when you factor in lost productivity and restoration. For many UK SMEs, these hidden expenses are far more damaging than the ransom itself. Following a professional ransomware prevention checklist is the most cost-effective way to avoid these business-ending financial burdens.
Posted on: August 11th, 2026 by Cornerstone
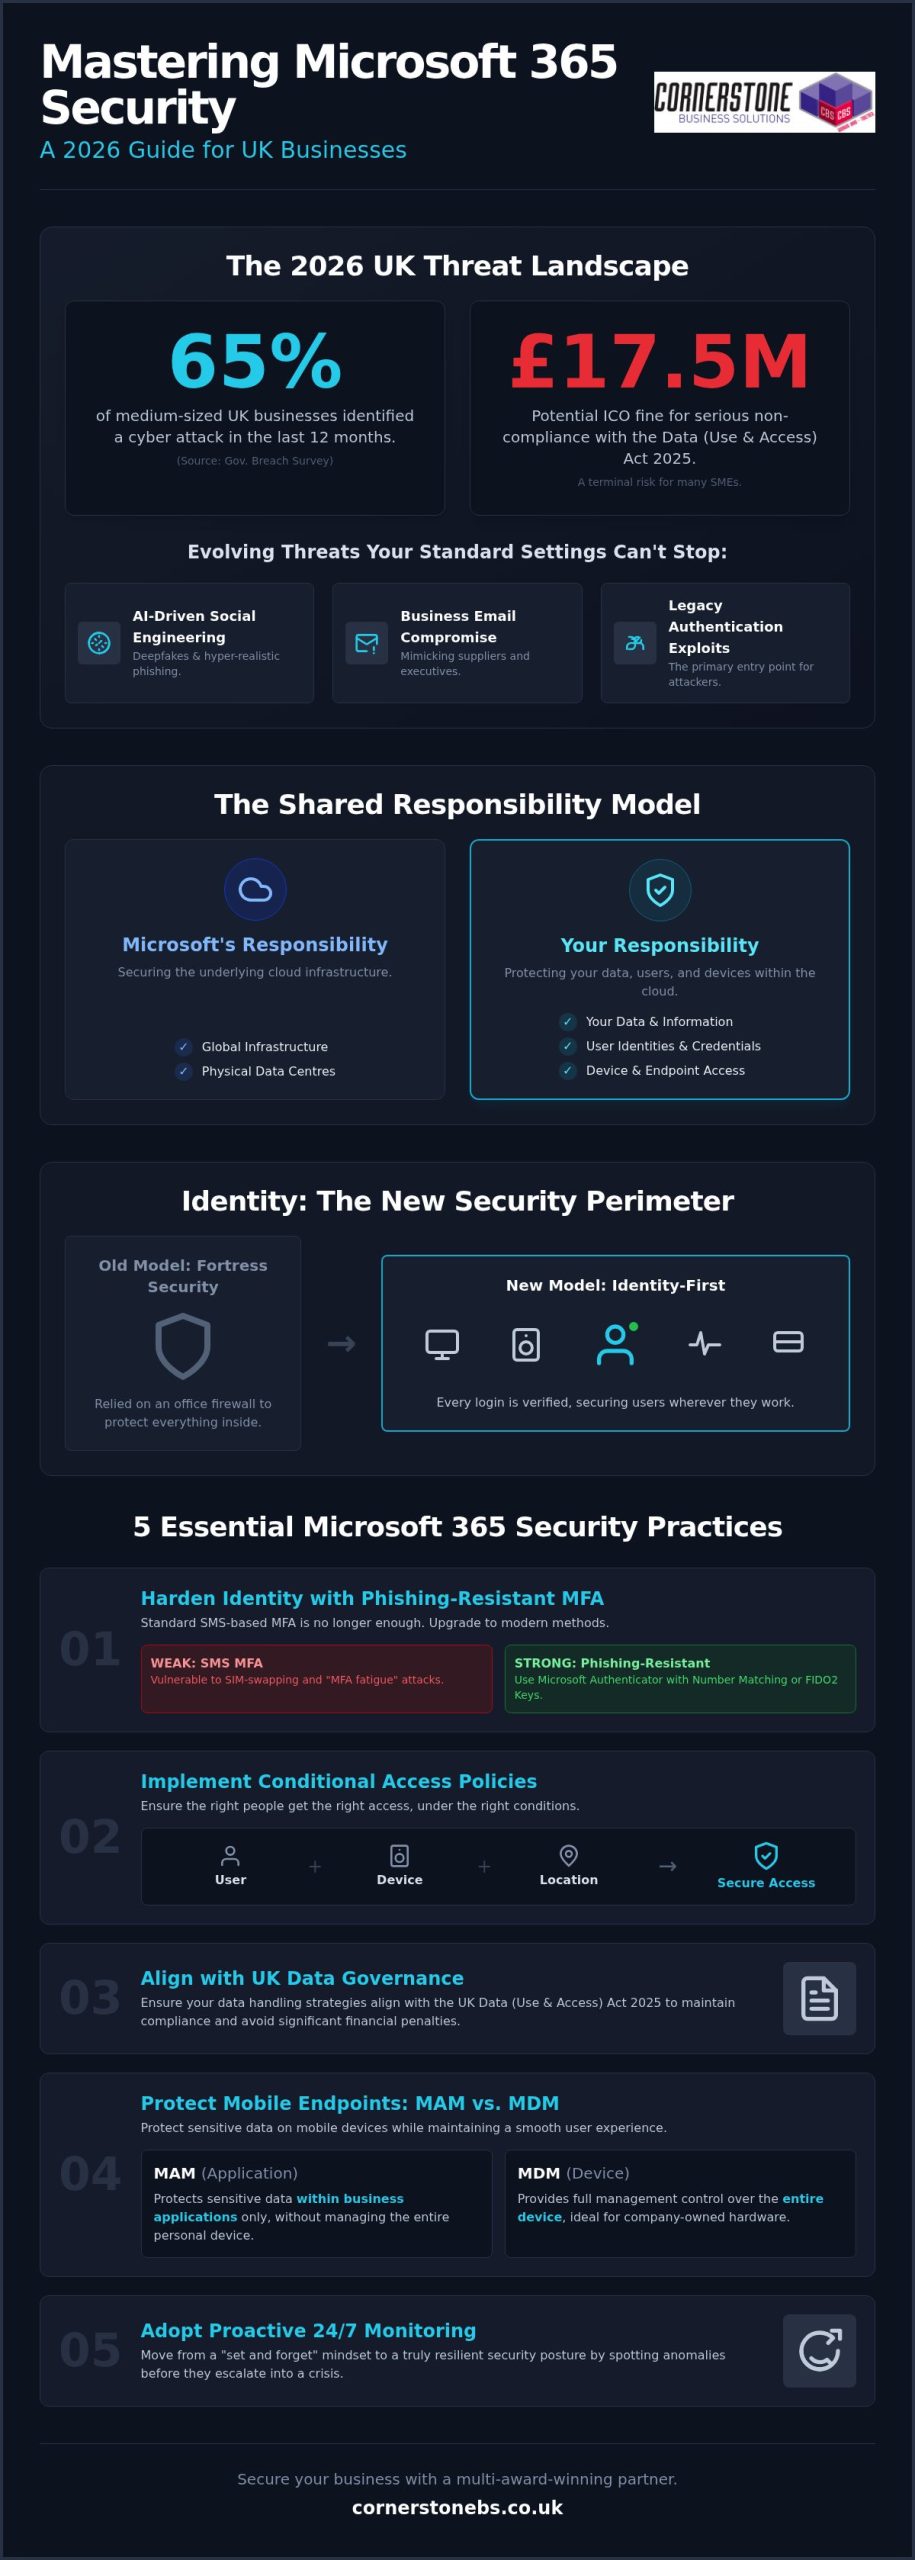
Did you know that 65% of medium-sized UK businesses identified a cyber attack in the last 12 months? It is a sobering statistic from the latest Government breach survey, and it makes implementing robust microsoft 365 security best practices for uk business more critical than ever. You likely feel the pressure of staying compliant with the new Data (Use and Access) Act 2025 while trying to decode which Microsoft licenses actually offer the protection you need. It is frustrating to manage complex settings when you should be focusing on leading your team.
We believe security should be proactive and empowering, not a source of constant stress. You deserve to know your data is safe from the £17.5 million fine potential of the ICO without spending every weekend in an admin portal. As a multi-award-winning partner, we are here to simplify the technical jargon into a strategy that actually works for your specific regional operations and goals.
This 2026 guide will help you master your security configurations from the ground up. We will cover everything from NCSC-backed passwordless logins to the latest Microsoft Teams protection updates. By the end, you will have a clear, actionable roadmap to ensure your business remains secure, compliant, and resilient in a changing digital landscape.
Key Takeaways
- Identify the critical gaps in your current setup by mastering microsoft 365 security best practices for uk business that move beyond standard, out-of-the-box settings.
- Learn how to implement phishing-resistant authentication and essential Conditional Access policies to secure your business identity against AI-driven social engineering.
- Ensure your data governance strategies align with the latest UK Data (Use and Access) Act 2025 to maintain compliance and avoid significant financial penalties.
- Discover the difference between MAM and MDM to protect sensitive business information on mobile devices while maintaining a smooth experience for your team.
- Understand why proactive, 24/7 monitoring is the only way to move from a “set and forget” mindset to a truly resilient security posture.
The 2026 UK Threat Landscape: Why Standard Microsoft 365 Settings Aren’t Enough
Standard Microsoft 365 settings are built for convenience, not a 2026 threat environment. Relying on “out-of-the-box” configurations leaves your business exposed to sophisticated attacks that simple filters can’t catch. We’ve seen a massive shift toward AI-driven social engineering where hackers use deepfake technology to impersonate executives and trusted partners. Adopting microsoft 365 security best practices for uk business isn’t just a technical task; it’s a vital step to protect your local reputation and bottom line. A breach isn’t just an IT headache. Under the Data (Use and Access) Act 2025, the ICO can issue fines up to £17.5 million for serious non-compliance. For a UK SME, that financial hit combined with a lost reputation can be terminal.
Understanding the Shared Responsibility Model
A common mistake many UK directors make is assuming that Microsoft is responsible for all aspects of cloud safety. This isn’t the case. While Microsoft manages the physical data centres and global infrastructure, you are responsible for the data you store and the people who access it. Learning the basics of cloud security fundamentals helps you see where Microsoft’s job ends and yours begins. Without proper configuration, your sensitive files are essentially sitting in a secure building with the front door left unlocked.
The Shared Responsibility Model is a framework where Microsoft secures the underlying cloud infrastructure while you remain fully responsible for protecting your data, user identities, and device access.
Evolution of Cyber Threats in 2026
The 2026 threat landscape is dominated by Business Email Compromise (BEC) and “Shadow AI” risks. According to the UK Government Cyber Security Breaches Survey 2025/2026, 65% of medium-sized businesses identified a breach last year. Hackers no longer just send “dodgy” links; they use AI to draft perfectly phrased emails that mimic your suppliers. Legacy authentication remains the primary entry point for these criminals, as it lacks the modern safeguards needed to stop credential theft. Integrating professional cyber security services provides the proactive monitoring required to spot these anomalies before they escalate into a full-scale crisis.
Identity is now the new perimeter. We’ve moved past the days when a strong office firewall was enough. In a remote or hybrid world, your users’ credentials are the only thing standing between a hacker and your financial records. If you don’t secure the identity, you don’t have a perimeter. This identity-first approach ensures that every login attempt is verified, regardless of where the employee is working in the UK. It’s about moving from a reactive “on/off” switch to a proactive, identity-first governance model.
Hardening Identity: Implementing MFA and Conditional Access
Identity is the foundation of your digital estate. If a hacker steals a password, they essentially have a key to your office. In 2026, relying on a password alone is a massive risk. Implementing microsoft 365 security best practices for uk business starts with a robust identity strategy that assumes every login attempt could be a threat. We’ve moved past simple security; we now need “Identity-First” governance that verifies every user, every time, from every location.
Phishing-Resistant Multi-Factor Authentication
SMS-based multi-factor authentication (MFA) is no longer sufficient. Cybercriminals now use “MFA fatigue” attacks and SIM swapping to bypass these basic checks. For 2026, we recommend phishing-resistant methods. Microsoft Authenticator with Number Matching is now the standard. It requires the user to enter a specific code shown on the login screen into their phone app. This simple step prevents accidental approvals. For high-privilege accounts, like your global admins, using FIDO2 security keys provides the highest level of protection available. These physical keys ensure that even if a user is tricked by a fake login page, the attacker cannot gain access.
Conditional Access: The “If/Then” of Security
Conditional Access is the most powerful tool in your security arsenal. Think of it as an intelligent security guard that evaluates every login based on specific rules. It uses “If/Then” logic: If a user is logging in from an unknown country, then block access. For most UK SMEs, restricting logins to UK-only IP addresses is a quick win that stops thousands of automated offshore attacks. When planning a Microsoft 365 migration for business UK, auditing your existing identities and setting these rules early is vital for long-term stability.
Every UK business should implement these five essential Conditional Access policies:
- Require MFA for all users: No exceptions, especially for guest accounts.
- Block legacy authentication: Disable older protocols like IMAP or POP3 that hackers use to bypass MFA.
- Geo-blocking: Restrict access to the UK unless your staff are actively travelling.
- Device Compliance: Only allow access from managed, healthy devices that meet your security standards.
- Risk-based sign-ins: Automatically block or challenge “impossible travel” attempts, such as a login from London followed by one from New York ten minutes later.
Eliminating legacy authentication is a non-negotiable step. These older protocols are the #1 entry point for credential theft because they simply don’t support modern MFA. By turning them off, you close a massive door that attackers love to exploit. If you’re unsure where to start with these configurations, our team can help you review your current identity posture to ensure you’re fully protected.
Data governance is often the missing piece in microsoft 365 security best practices for uk business. While hardening your identity stops intruders at the front door, governance ensures that your sensitive information doesn’t slip out through the back. With the Data (Use and Access) Act 2025 now in full effect, the Information Commissioner’s Office (ICO) has enhanced powers to penalise businesses that fail to manage data complaints or protect personal records. Proper configuration within Microsoft 365 isn’t just about safety; it’s about staying on the right side of UK law.
UK GDPR and Cyber Essentials Alignment
Data Loss Prevention (DLP) Strategies
Data Loss Prevention acts like a digital sieve, catching sensitive information before it leaves your network. We recommend setting up specific DLP policies that scan for UK-specific identifiers, such as National Insurance numbers and credit card details. If an employee tries to email a spreadsheet containing these details to a personal address, the system can automatically block the message or prompt for a justification. When we build bespoke cloud solutions for our partners, we prioritise these internal safeguards to mitigate the risk of “insider threats,” whether they are malicious or just accidental mistakes.
To truly master your data lifecycle, you should implement these three core governance tools:
- Sensitivity Labels: Tag documents as “Confidential” or “Internal Only.” These labels follow the file wherever it goes, ensuring encryption remains active even if the document is shared externally.
- Automated Retention Policies: UK GDPR requires that you don’t keep data longer than necessary. Set policies to automatically delete old CVs or project files after a set period, reducing your “data surface area” in the event of a breach.
- Bulk-Download Alerts: Configure Microsoft Defender for Cloud Apps to trigger an alert if a user suddenly downloads an unusual volume of files. This is often the first sign of an employee preparing to leave or a compromised account.
Managing these settings manually can be a full-time job. By automating your retention and labelling, you take the guesswork out of compliance. It gives you the peace of mind that your business is meeting its legal obligations without requiring constant manual intervention from your team.
Endpoint and Collaboration Security: Protecting Teams and Devices
Securing your identity and data is only half the battle. Your employees interact with your business every day through endpoints: laptops, smartphones, and collaboration tools like Microsoft Teams. Implementing microsoft 365 security best practices for uk business means extending your protection to these digital workspaces. In 2026, hackers have shifted their focus to high-trust environments where users are more likely to click a link or download a file without a second thought. This makes the security of your collaboration apps just as vital as your office firewall.
Securing the “New Office”: Microsoft Teams
Microsoft Teams has become the primary hub for UK business communication. However, its default settings often allow external users to initiate contact, opening the door for sophisticated social engineering. As of January 12, 2026, Microsoft Teams automatically blocks high-risk file types by default, but you must still manage your guest access permissions. We recommend using private channels for sensitive department data to ensure that only specific team members can view financial or HR documents. Monitoring for malicious files is essential, as phishing remains the most common attack vector for UK organisations according to the 2026 Cyber Security Breaches Survey.
Managing the Remote Workforce with Intune
The rise of hybrid work across the UK has made the “Bring Your Own Device” (BYOD) model a standard practice. This creates a unique challenge: how do you protect business data on a personal phone? This is where the choice between Mobile Device Management (MDM) and Mobile Application Management (MAM) becomes vital. MDM gives you full control over a company-owned laptop, allowing for “Remote Wipe” capabilities if hardware is lost on a commute or stolen. MAM, however, allows you to secure only the business apps like Outlook and Teams on an employee’s personal device without touching their private photos or messages.
Enforcing BitLocker encryption on all business laptops is a non-negotiable step for 2026. Microsoft Defender for Business now provides enterprise-grade protection for SMEs, identifying vulnerabilities before they are exploited. Managing this level of detail across a growing team can be overwhelming. Our it company solutions simplify this process by automating device enrollment and policy enforcement. This ensures every device that touches your network is healthy and compliant from day one. If you want to ensure your remote team is truly secure, reach out to our local experts for a comprehensive device security audit today.
Proactive Protection: How Managed IT Support Sustains Your Security
Many businesses mistakenly believe that ticking the boxes for MFA and DLP means the security job is finished. It isn’t. Maintaining microsoft 365 security best practices for uk business is an ongoing journey that requires constant adjustments as the 2026 threat landscape shifts. A “set and forget” mindset often leads to configuration drift, where small changes over time create massive gaps in your defense. Proactive management ensures your settings stay hardened against new vulnerabilities the moment they emerge.
The Value of Continuous Security Monitoring
Microsoft 365 produces thousands of log entries every hour. While AI filters catch obvious threats, sophisticated attackers often hide in the “grey area” of legitimate-looking activity. Human expert analysis is what turns raw data into actionable intelligence. By leveraging specialised managed IT services, you gain access to specialists who monitor these patterns around the clock across the UK. This proactive stance slashes your Mean Time to Detect (MTTD), ensuring that if an anomaly occurs, it is neutralised before it can cause reputational damage or lead to a heavy ICO fine. Rapid incident response is the difference between a minor blip and a total system shutdown.
Building a Human Firewall
Your employees are your greatest asset, but they can also be your biggest vulnerability if they aren’t prepared for modern social engineering. We focus on bridging the gap between technical configurations and user behaviour. This involves ongoing security awareness training that feels relevant and accessible, rather than a dry compliance exercise. We use simulated phishing attacks to give your team hands-on experience in spotting the latest AI-generated lures. These simulations identify which staff members might need extra support, allowing us to strengthen your “human firewall” before a real attacker comes calling. Professional IT support is a foundational investment in your business stability and emotional security, providing the expert oversight needed to let you focus on your core goals.
Regular security audits are the final piece of the puzzle. These deep dives ensure your tenant remains aligned with the latest NCSC guidance and UK GDPR requirements. We don’t just look at the switches and toggles; we look at how your people interact with data every day. This holistic approach ensures that your Microsoft 365 environment remains a secure, productive space that supports your long-term growth. If you are ready to move beyond basic settings and embrace a truly resilient strategy, Cornerstone Business Solutions is here to guide you every step of the way.
Securing Your Business Future in a Changing Landscape
Securing your business for the challenges of 2026 is an ongoing journey, not a one-time task. We’ve explored why standard settings aren’t enough and how hardening your identity with phishing-resistant MFA is now a non-negotiable step. By aligning your data governance with the latest UK regulations, you protect both your reputation and your bottom line. Implementing microsoft 365 security best practices for uk business ensures that your team can collaborate safely without the fear of a costly breach.
As an Official Microsoft Partner, we pride ourselves on being more than just a provider; we’re your long-term security ally. Our multi-award-winning IT support team provides proactive 24/7 system monitoring to catch threats before they impact your operations. You don’t have to manage these complex configurations alone. We invite you to Book your expert Microsoft 365 security audit with Cornerstone Business Solutions today and take the first step toward total peace of mind. Let’s work together to build a resilient and secure future for your business.
Frequently Asked Questions
How much does Microsoft 365 security cost for a UK business?
The cost of security is primarily determined by your license choice. As of July 2026, Microsoft 365 Business Premium costs £16.90 per user per month, while Enterprise E5 is £47.80. While basic security features are included in lower tiers, the advanced protection needed for microsoft 365 security best practices for uk business typically requires the Premium or E5 levels. You should also factor in professional management to ensure these tools are configured correctly.
Is Microsoft 365 GDPR compliant for UK companies?
Microsoft 365 provides the tools to be GDPR compliant, but it isn’t compliant “out of the box.” You are responsible for configuring data residency, retention policies, and access controls. With the Data (Use and Access) Act 2025 now in force, you must use Microsoft Purview to manage Subject Access Requests and acknowledge them within 30 days. Compliance is a shared effort between the platform’s infrastructure and your specific internal settings.
What is the difference between Microsoft 365 Business Premium and Standard security?
Business Standard focuses on productivity apps and basic cloud storage. Business Premium is the true security tier for SMEs, adding Microsoft Intune for device management and Defender for Business for endpoint protection. Crucially, Premium includes Conditional Access, which allows you to set “If/Then” rules for logins. This makes it the minimum recommended level for any UK business that needs to protect sensitive data and manage a remote workforce effectively.
Can I secure Microsoft 365 without an IT department?
You can technically enable basic settings yourself, but the complexity of modern threats makes this risky for most business owners. Missing a single toggle in the admin portal can leave your data exposed to AI-driven phishing. Most UK SMEs find that partnering with a local expert is more efficient than hiring a full internal team. It provides the peace of mind that your systems are monitored 24/7 by specialists who understand the 2026 landscape.
How often should we perform a Microsoft 365 security audit?
We recommend a comprehensive security audit at least once a year. However, if you operate in the legal or financial sectors, quarterly reviews are much safer. Frequent audits help you stay ahead of “configuration drift,” where small changes by users or new feature releases create unintended vulnerabilities. Regular check-ups ensure your microsoft 365 security best practices for uk business remain aligned with the latest NCSC guidance and evolving cyber threats.
What is the best way to prevent ransomware in Microsoft 365?
Preventing ransomware requires a multi-layered approach. Start by enforcing phishing-resistant MFA and blocking legacy authentication protocols that hackers use to bypass security. Microsoft Defender for Business plays a vital role by identifying and isolating suspicious file behaviour in real-time. Combining these technical controls with regular employee awareness training creates a “human firewall” that is significantly harder for ransomware groups to penetrate. Proactive monitoring is your best defense against these attacks.
Does Microsoft 365 backup my data automatically?
No, Microsoft does not provide a traditional backup for your data. They ensure the service is available, but they aren’t responsible for data lost due to accidental deletion or ransomware. You need a dedicated Disaster Recovery solution to ensure your emails and files are recoverable. Relying solely on the Recycle Bin is a dangerous strategy that leaves your business vulnerable to permanent data loss if a breach occurs or a file is corrupted.
Is MFA mandatory for UK businesses using Microsoft 365?
While not a legal requirement for all, MFA is now a “pass or fail” requirement for Cyber Essentials certification as of April 2026. This means if you want to bid for government contracts or demonstrate a high level of security to your clients, MFA is mandatory. Beyond certification, the NCSC strongly advises all organisations to adopt it. It is the single most effective way to stop 99% of bulk credential attacks today.
Posted on: August 1st, 2026 by Cornerstone
Did you know that 43% of UK businesses identified a cyber breach or attack in the last year? That represents approximately 612,000 organisations facing digital disruption. As a business leader, you likely feel the weight of this reality. It is easy to feel overwhelmed by the rise of AI-powered phishing and the complexities of the new Cyber Security and Resilience Bill 2024-26. You want to focus on growth, but the fear of falling behind on threats can be a constant distraction.
Our cybersecurity blog uk provides the clarity you need to move forward with confidence. As a multi-award-winning provider, we believe security is a foundational element of your business stability. You deserve the emotional security that comes with knowing your systems are protected. This article delivers a clear roadmap for your 2026 security priorities. We will show you how to balance innovation with robust protection, covering everything from the NCSC “Cyber Shield” initiative to bespoke defensive strategies. Let’s explore how to ensure total operational resilience for your business.
Key Takeaways
- Shift your security focus from traditional network perimeters to identity-centric protection to ensure total operational resilience in the 2026 UK market.
- Learn how to leverage defensive AI and machine learning to neutralise hyper-personalised phishing attacks before they can disrupt your daily operations.
- Stay ahead of evolving regulations like the Cyber Security and Resilience Bill 2024-26 by following our cybersecurity blog uk for clear compliance roadmaps.
- Foster a proactive reporting culture by replacing outdated annual training with continuous micro-learning that empowers your team to act as a human firewall.
- Understand the strategic ROI of managed security services to bridge the 2026 skills gap and provide the foundational stability your business needs to thrive.
The UK Cyber Security Landscape: What Business Leaders Need to Know
Business leaders often ask us what resilience actually looks like in 2026. In our cybersecurity blog uk, we define it as more than just surviving an attack. It is about maintaining operational continuity while under fire. The 2026 UK market is faster and more connected than ever. This means a breach at one small supplier can ripple through an entire supply chain, making security a foundational element of your business stability. You need to view your digital defences as the bedrock of your company’s future.
The Evolution of Ransomware 2.0
Ransomware has matured. It’s no longer just about locking your files. We now see triple-extortion tactics where criminals encrypt data, steal it to leak later, and then harass your clients or partners directly. With Ransomware-as-a-Service (RaaS), even low-skilled attackers can launch devastating campaigns for a small fee. Relying on traditional backups is a dangerous gamble. If the attacker has already spent weeks inside your network, your backups might already be compromised or deleted before the encryption even begins.
Identity is the New Perimeter
The days of the office firewall being your only shield are over. With hybrid working now the standard across Britain, your perimeter exists wherever your employees log in. This is why the National Cyber Security Centre (NCSC) champions a Zero Trust architecture. We are seeing a massive shift toward password-less authentication. It is more secure and less frustrating for your team. Identity is the new gatekeeper. If a criminal steals a valid login, your firewall will simply wave them through without a second thought.
The Cost of Inaction
A breach costs more than just the immediate recovery fee. Think about the lost productivity while your team sits idle. Consider the £ thousands in potential regulatory fines or the cost of rebuilding a tarnished reputation in a tight-knit local community. These hidden expenses often dwarf the initial ransom demand. Cyber Resilience is the ability to operate through an attack. Investing in bespoke stability today prevents the emotional and financial drain of a crisis tomorrow, ensuring your business remains a reliable partner for your clients.
The AI Revolution: Securing Your Business in the Age of Automation
AI has completely changed the rules of the game for UK business leaders. It is no longer just a tool for productivity. It is the new front line in digital warfare. Criminals now use Large Language Models (LLMs) to automate the most difficult parts of a cyberattack. This makes the insights in our cybersecurity blog uk essential for staying ahead of the curve. While your team uses AI to write reports, attackers use it to craft hyper-personalised phishing campaigns that bypass traditional filters. They can generate thousands of unique, convincing emails in seconds, tailored specifically to your employees’ roles.
Fighting back requires the same technology. Defensive AI uses machine learning to identify patterns and anomalies across your network in real-time. It doesn’t sleep and it doesn’t get tired. This proactive stance is a core part of the Government Cyber Security Strategy. By using AI to monitor for threats, you gain the ability to neutralise an attack before it causes operational downtime. It provides the foundational stability that every modern business needs to grow safely.
Combating AI-Generated Phishing
The old advice of “looking for typos” is now obsolete. AI-generated emails are grammatically perfect and often mimic the exact tone of your suppliers. We are also seeing a rise in deepfake audio and video used in business email compromise. A voice note that sounds exactly like your finance director could be a sophisticated AI clone. To stay secure, you need AI-driven security filters. These tools look beyond the text. They analyse communication metadata and sender history to flag suspicious activity that a human would likely miss.
Establishing an AI Governance Framework
Many UK offices are currently dealing with “Shadow AI.” This occurs when staff use public AI tools without official approval or oversight. If an employee pastes proprietary business data into a public model, that information could potentially be leaked or used to train the AI. You must establish a clear governance framework. This includes setting strict policies for data input and ensuring tools like Microsoft Copilot are configured for maximum privacy. Your AI safety is deeply connected to your cloud solutions, which provide the secure environment your data lives in. If you want to ensure your AI adoption doesn’t compromise your security, we’d be happy to have a quick conversation about your current setup.
UK Compliance and Regulation: Navigating the 2026 Framework
Compliance shouldn’t feel like a burden. In our cybersecurity blog uk, we see it as a framework for stability. The 2026 Cyber Security and Resilience Bill represents a major shift in our national policy. It expands the scope of regulation to include data centres and managed service providers. For many UK firms, this means stricter oversight and higher stakes. 31% of businesses now have board-level responsibility for cyber security. This isn’t just an IT problem anymore; it is a leadership priority that ensures your organisation remains a trusted partner.
GDPR remains your foundation for data privacy. It sets the standard for how you handle sensitive information. However, Cyber Essentials is now the prerequisite for many UK contracts. Government data shows certification rose to 5% in 2026. This badge tells your clients you take their safety seriously. It’s a simple way to build trust in a competitive market. When you align with these standards, you aren’t just following rules. You are building a resilient business that can weather any digital storm.
Understanding the NIS2 Directive in the UK
NIS2 is no longer just for big utility companies. It now includes ‘important’ entities across sectors like food production and postal services. If you fall into this category, management faces personal liability for security failures. You can’t delegate the blame to your technical team. The reporting rules are also much tighter. You must provide an early warning within 24 hours of identifying a significant incident. This requires a highly organised response plan that works under pressure, giving you the clarity to act fast when it matters most.
Securing the Supply Chain
Your partners’ security is now your legal responsibility. If a supplier has a breach, the regulator will look closely at your due diligence. You need to conduct regular third-party risk assessments to find weak links. This shouldn’t be a tick-box exercise. It’s about ensuring every organisation you connect with is as secure as you are. Integrating these checks into your broader cyber security services strategy keeps you ahead of the curve. Preparing for an audit doesn’t have to disrupt your daily operations. With bespoke audits and proactive monitoring, you can prove your compliance and maintain your peace of mind.
The Human Element: Building a Security-First Culture
Your team shouldn’t be viewed as your greatest vulnerability. In this cybersecurity blog uk, we advocate for turning your staff into your most effective defensive layer. Most breaches still involve a human element, but the answer isn’t more restrictive software. It’s about culture. A ‘blame culture’ encourages people to hide their mistakes, which gives attackers more time to move through your systems. Instead, you need a ‘reporting culture’ where an employee feels confident flagging a suspicious email immediately without fear of reprisal. This transparency is a foundational element of business stability.
Annual training sessions are a thing of the past. They are too slow for the 2026 threat landscape and often feel like a box-ticking exercise. We recommend continuous micro-learning that fits into the busy workday. Short, punchy videos and quick quizzes keep security at the front of the mind. Gamification makes this process engaging rather than a chore. When security becomes a shared responsibility, your business gains a level of stability that technology alone cannot provide. Empowered employees act as a human firewall, protecting your data and your reputation.
Modern Security Awareness Training
The Role of Leadership in Security
Security must start at the top. It should be a standing item on every board agenda, treated with the same weight as financial performance or growth strategies. When employees see the C-suite using Multi-Factor Authentication (MFA) and following every policy, they follow suit. Executive buy-in transforms security from an IT requirement into a core company value. This leadership creates an atmosphere of trust and reliability that permeates the entire organisation. Leading by example is the most powerful tool you have to protect your firm’s future. If you’re ready to empower your team, our experts can help you design a bespoke cyber security training roadmap for your staff.
Managed Security: The Strategic Foundation for 2026
Hiring a dedicated cybersecurity expert in the UK has never been more difficult. The 2026 skills gap means small and medium-sized firms are competing with global giants for a tiny pool of talent. This is why our cybersecurity blog uk highlights managed security as a strategic necessity rather than an optional extra. By partnering with a multi-award-winning provider, you gain a full team of specialists for a fraction of the cost of one full-time hire. This provides the foundational stability your business needs to scale without the constant worry of a hidden vulnerability.
Reactive repair is the most expensive way to handle IT. You’re paying for emergency call-outs and dealing with the £ thousands lost during downtime. Proactive monitoring identifies a threat before it becomes a crisis. It’s about total operational resilience. We provide 24/7/365 security operations, giving you the emotional security to sleep soundly while we watch the gates. Bespoke technology solutions ensure that as your business grows, your protection grows with it. You shouldn’t have to choose between innovation and safety.
The Benefits of a Managed Security Provider
You get access to enterprise-grade tools that are usually reserved for the biggest corporations. We monitor your systems continuously, providing rapid incident response that stops attacks in their tracks. These services integrate seamlessly with your Managed IT support. This creates a unified front where your digital infrastructure and your security work in perfect harmony. It simplifies your management and ensures that no part of your network is left exposed to the 2026 threat landscape.
Getting Started with a Security Audit
Every journey to resilience starts with a comprehensive assessment. During a bespoke cyber security audit, we look at your entire stack to identify and prioritise vulnerabilities. We don’t just give you a list of problems; we provide a clear roadmap for improvement. This allows for a smooth transition to resilient IT company solutions that are focused on your specific goals. It is about moving from a state of uncertainty to a position of strength. We invite you to have an informal conversation with our local team to see how we can secure your firm’s future together.
Building a Resilient Future for Your Business
The 2026 threat landscape is undeniably complex, but it shouldn’t hold your organisation back. We’ve explored how identity has replaced the traditional perimeter and why AI governance is now a leadership priority. By moving toward a proactive reporting culture and embracing managed security, you turn digital defence into a competitive advantage. This cybersecurity blog uk is designed to help you simplify these technical challenges so you can focus on what you do best: growing your company.
As a multi-award-winning UK IT provider, we understand the specific needs of regional businesses. Our strategic partnerships with Microsoft and Cisco allow us to deliver enterprise-grade protection with a personal, local touch. Whether you need one of our bespoke security audits or a complete infrastructure overhaul, we are here to act as your dedicated long-term partner. You don’t have to navigate these changes alone.
We invite you to book a friendly chat with our security experts today. Let’s discuss how we can provide the foundational stability and emotional security your organisation deserves. Your business has a bright future, and we’re ready to help you protect it.
Frequently Asked Questions
What is the most common cyber attack in the UK today?
Phishing remains the most prevalent threat facing UK organisations. According to the 2026 Cyber Security Breaches Survey, 38% of businesses identified phishing as their primary attack vector. These attacks are no longer just poorly written emails; they are now hyper-personalised messages often crafted by AI to deceive even the most vigilant staff. Maintaining a security-first culture is your best defence against these evolving social engineering tactics.
Is Cyber Essentials certification mandatory for all UK businesses?
Certification is not mandatory for every business, but it is increasingly becoming a prerequisite for winning UK government contracts and joining major supply chains. Holding this certification demonstrates that you have implemented the five technical controls required to protect against the most common digital threats. It provides a foundational level of stability that reassures your partners and clients that their data is in safe hands.
How much should a UK SME spend on cyber security in 2026?
There is no single figure, but most experts suggest allocating between 10% and 15% of your total IT budget to security. In 2026, this investment should focus on proactive monitoring and identity-centric protection rather than just reactive repairs. Viewing this as a strategic foundation for growth ensures your business remains resilient. We recommend a bespoke audit to help prioritise your spending where it will have the most impact.
What is the difference between a firewall and an EDR solution?
A firewall acts as a digital perimeter fence, filtering traffic entering and leaving your network. Endpoint Detection and Response (EDR) is more like a security guard inside your building. EDR monitors individual devices, such as laptops and servers, for suspicious behaviour in real-time. While firewalls are essential, EDR is critical for catching threats that have already bypassed your perimeter, providing a much deeper level of protection for hybrid teams.
How does the UK’s PSTN switch-off affect my business security?
The switch-off means all legacy analogue phone lines are being replaced by digital, internet-based systems like VoIP. From a security perspective, this move requires you to ensure your new digital voice infrastructure is properly encrypted and integrated into your broader defensive strategy. It is a great opportunity to modernise your communication while strengthening your digital resilience. We help firms transition safely to avoid any vulnerabilities during the migration.
Can AI completely replace human cyber security experts?
AI is a powerful tool for processing data and identifying patterns at scale, but it cannot replace human expertise. Effective security requires the context and nuanced decision-making that only a human professional can provide. In our cybersecurity blog uk, we advocate for a collaborative approach where AI handles the heavy lifting of threat detection, allowing our expert team to focus on strategic response and bespoke risk management.
What are the first steps to take after a data breach occurs?
Your first priority is to contain the breach by isolating affected systems to prevent further spread. Once contained, you must assess the extent of the data loss and follow your incident response plan. Under the 2026 framework, you may need to provide an early warning to regulators within 24 hours. Clear communication with your team and legal advisors is essential to maintain emotional security and manage reputational impact during the recovery process.
Is multi-factor authentication (MFA) really enough to stop hackers?
Multi-factor authentication is one of the most effective ways to block unauthorised access, stopping the vast majority of automated attacks. However, it is not a silver bullet. Sophisticated criminals now use “MFA fatigue” and session hijacking to bypass these prompts. While MFA is a non-negotiable standard for 2026, it must be paired with conditional access policies and continuous staff training to ensure total operational resilience for your organisation.
Posted on: July 30th, 2026 by Cornerstone
Did you know that 70% of medium-sized UK businesses faced a cyberattack in the last 12 months? With 80% of breaches now involving stolen credentials, the old way of defending your network perimeter is no longer enough. You might feel overwhelmed by technical jargon or worried about meeting strict NIS2 and DORA standards. It’s a common challenge, especially when you need to justify every penny of security spend to your board. Starting with a thorough zero trust assessment is the most effective way to move from a reactive security model to a proactive, data-centric fortress.
We understand that as a business leader, you want clarity and resilience rather than more complexity. We’re here to act as your dedicated partner, simplifying these high-tech concepts into a clear roadmap for your team. This guide helps you validate your current investments and achieve total compliance readiness. We’ll explore the NCSC design principles and the CISA 2.0 maturity model to simplify the path forward. By the end, you’ll see how shifting to a “never trust, always verify” model protects your growth and provides the stability you need to lead with confidence.
Key Takeaways
- Adopt a “never trust, always verify” mindset to replace outdated perimeter defences with modern, identity-based security.
- Conduct a zero trust assessment to map out your digital environment across six essential pillars, ensuring every device and user is validated.
- Move from reactive, manual security to automated resilience by understanding your position on the Zero Trust Maturity Model.
- Simplify compliance with NIS2 and DORA by creating a clear, evidence-based roadmap that justifies your security investments.
- Work with a multi-award-winning regional partner to translate technical data into a robust, long-term strategy for business continuity.
What is Zero Trust Assessment & Why is it Vital in 2026?
The days of relying on a strong office firewall are over. In 2026, your team works from home, coffee shops, and client sites, meaning your data lives everywhere. This shift has made traditional perimeter security obsolete. Zero Trust is the modern answer. It moves away from the old “trust but verify” approach to a stricter “never trust, always verify” model. A zero trust assessment acts as a deep-dive audit of your entire digital environment. It evaluates how you handle identities, devices, and data against the latest security standards.
A zero trust assessment is a strategic roadmap that transforms your security posture into a proactive, data-centric fortress for modern cyber resilience. By examining your infrastructure through the lens of Zero Trust Architecture, we help you identify hidden vulnerabilities before they can be exploited. This isn’t just about ticking boxes; it’s about building a foundation that supports your business growth without compromising on safety.
The Core Philosophy: Never Trust, Always Verify
The heart of this model rests on three non-negotiable pillars. First, you must verify explicitly by always authenticating based on all available data points. Second, you use least privileged access to limit user permissions to only what’s necessary for their specific role. Finally, you assume breach. This means you design your systems as if an attacker is already inside. These principles significantly reduce the “blast radius” of any potential incident, ensuring one compromised password doesn’t lead to a total system failure. For a deeper look at how these layers protect you, explore our cyber security services designed for UK businesses.
Business Benefits Beyond Security
While protection is the primary goal, a zero trust assessment delivers massive operational wins. It streamlines user access, making it easier for your team to get what they need without jumping through unnecessary hoops. It’s also a powerful tool for meeting strict UK and international standards like NIS2 or DORA. Beyond compliance, it improves the daily employee experience. When security is seamless, your staff can work from anywhere with total confidence, knowing their tools are as mobile as they are. You get a more efficient workforce and a board that’s happy to see clear, validated returns on security spending.
The 6 Pillars of a Comprehensive Zero Trust Audit
A zero trust assessment isn’t just a quick scan of your firewall. It’s a holistic review of your entire digital ecosystem. To build a truly resilient business, we evaluate your infrastructure across several interconnected domains. This framework is largely built upon the NIST Special Publication 800-207, which serves as the global gold standard for modern security. By looking at these pillars individually, we ensure no stone is left unturned in your defence strategy.
- Identity: This is your new perimeter. We verify every user through phishing-resistant multi-factor authentication (MFA) to ensure they are exactly who they claim to be before granting access.
- Devices: Whether it’s a company-issued laptop or a staff member’s mobile, we monitor the health and compliance of every endpoint. If a device isn’t up to date, it doesn’t get in.
- Applications: We secure the software and APIs your business relies on. This prevents “shadow IT” and ensures that data only flows through authorised, secure channels.
- Data: Your information is your most valuable asset. We help you classify and protect it with robust encryption, whether it’s stored on a local server or moving through the cloud.
- Infrastructure: We harden your servers, containers, and virtual environments. This proactive approach prevents unauthorised lateral movement if one part of your system is compromised.
Network and AI: The 2026 Frontiers
Traditional flat networks are a significant risk. Once an intruder gets past the front door, they can often roam freely. We focus on micro-segmentation, which creates secure internal zones to contain potential threats and protect your most sensitive areas. In 2026, your zero trust assessment must also account for the AI pillar. We ensure your team isn’t accidentally leaking proprietary data into public AI models while defending you against AI-powered phishing attacks. AI-driven assessments identify anomalies faster than manual audits, catching subtle patterns that human eyes might miss.
Mapping Pillars to Your Current Infrastructure
The real value of an audit lies in identifying your weakest links. You might have excellent identity controls but find your device management is lagging. Achieving a unified security posture requires cross-pillar visibility, where every layer of your defence communicates with the others. This joined-up thinking is the foundation of our managed IT services, where we handle the technical heavy lifting so you can focus on growth. If you want to see how these pillars fit your specific business needs, we’re always happy to have a chat about your security strategy.
Moving from theory to practice requires a structured approach. You can’t secure what you haven’t mapped, so a zero trust assessment begins with a clear, logical sequence. We follow a four-step methodology designed to give you total visibility without disrupting your daily operations. This process ensures your security strategy aligns with your actual business goals, rather than just technical checklists.
Step 2: Technical Execution. We use specialized tools like the Microsoft Zero Trust Assessment PowerShell module to pull raw configuration data. This provides a snapshot of your current security settings across identity, endpoints, and apps.
Step 3: Stakeholder Interviews. Tech only tells half the story. We talk to your team to understand how data actually flows through your business. This helps us spot “shadow IT” or manual workarounds that scripts might miss.
Step 4: Gap Analysis. Finally, we compare your “as-is” setup against “to-be” best practices. We use benchmarks like CISA’s Zero Trust Maturity Model to show exactly where you stand and what needs to change.
Automated vs. Expert-Led Assessments
Open-source PowerShell scripts are excellent for a quick health check. They’re fast and provide a wealth of data. However, they often return complex errors or technical flags that don’t account for your specific business logic. An automated tool might flag a vital legacy application as a risk, but it won’t tell you how to wrap it in a secure container. That’s where an expert-led audit adds real value. We provide a second pair of eyes to interpret the data, ensuring your security doesn’t become a barrier to productivity.
Key Tools for the 2026 Audit
We leverage the full power of the Microsoft stack to keep your audit precise. Microsoft Entra ID Protection helps us analyze identity risks, while Intune compliance checks ensure every mobile device meets your safety standards. We also utilize Azure Network security baselines to verify your cloud perimeters. For businesses looking to scale their infrastructure safely, our cloud solutions provide the perfect foundation for these advanced auditing tools. By combining these technologies, we create a zero trust assessment that’s both technically rigorous and business-focused.
Interpreting Your Results: The Zero Trust Maturity Model
Once your zero trust assessment is complete, you’re left with a wealth of technical data. The real challenge is turning those findings into a strategy your board can support. We use the maturity model to help you see exactly where you stand. Don’t worry if you aren’t at the top yet. Most UK businesses are currently moving through the earlier stages, and we’re here to guide you through each step of the journey.
- Traditional Stage: Your security is largely reactive. You likely have a flat network where an intruder can move freely once they bypass the initial login. Configurations are mostly manual, and you might still rely on basic passwords for legacy systems.
- Advanced Stage: You’ve started to automate your defences. You have basic multi-factor authentication (MFA) in place and have begun micro-segmenting your network to protect sensitive data. You’re starting to see a more proactive security posture.
- Optimal Stage: This is the gold standard for resilience. Your system makes dynamic, real-time access decisions based on user behaviour and device health. All data is fully encrypted, whether it’s sitting on a server or moving through the cloud.
Adopting an “Assumption of Breach” mindset is a massive shift for most leaders. It means we stop pretending your perimeter is impenetrable. Instead, we design your systems to contain an incident the moment it happens. This approach fundamentally changes your disaster recovery planning. It ensures that if one part of your system is compromised, your entire business doesn’t grind to a halt. You gain emotional security knowing that your most vital assets are protected by layers of verification.
Prioritising Remediation: The Quick Wins
We don’t expect you to fix everything overnight. We focus on high-impact, low-effort changes that deliver immediate results. Implementing robust Conditional Access policies is often the best place to start. By addressing the “Identity” pillar through phishing-resistant MFA, you build a solid foundation for the rest of your security journey. Security is a journey, not a destination, requiring continuous re-assessment to stay ahead of evolving threats.
Long-Term Strategic Planning
A successful transition takes time and careful budgeting. We help you build a 12-24 month roadmap that aligns your security goals with your business growth. Many organisations are now moving from heavy upfront hardware costs (CAPEX) to predictable, monthly service models (OPEX). This shift makes it easier to justify security spend while ensuring you always have the latest protection. You can find more about how we integrate these strategies into our IT company solutions for local businesses. Ready to see where your business sits on the maturity scale? Book your zero trust assessment with our expert team today.
Expert Zero Trust Implementation with Cornerstone Business Solutions
We’ve explored the technical pillars and the maturity stages of modern security. Now, it’s time to focus on the execution. Interpreting the results of a zero trust assessment requires more than just technical knowledge; it needs a partner who understands your specific business goals. As a multi-award-winning IT provider, we don’t just hand you a report and walk away. We act as your long-term partner, translating complex security data into a clear, actionable strategy that protects your growth.
Our proactive approach sets us apart. Many providers simply run a diagnostic tool and highlight the red flags. We go deeper. We look at why those vulnerabilities exist and how they impact your daily operations. Whether you’re a small local firm or a larger regional enterprise, we tailor our bespoke solutions to fit your industry and scale. We ensure that your security doesn’t become a barrier to productivity, but rather a foundation for it.
Beyond the Assessment: Managed Remediation
The real work begins once the audit is complete. Cornerstone handles the technical heavy lifting of hardening your systems so your team can stay focused on what they do best. By partnering with global leaders like Microsoft and Cisco, we deliver robust security systems that stand up to the 2026 threat landscape. You aren’t just getting a set of tools; you’re getting the peace of mind that comes from a dedicated, UK-wide support team. We ensure your security posture evolves as new threats emerge, keeping your business stable and secure year-round.
Ready to Secure Your Future?
Cyber security isn’t a one-time fix. It’s a foundational element of your business stability and emotional security. Our proactive IT maintenance plans integrate Zero Trust principles into your daily operations, ensuring you stay ahead of strict compliance requirements like NIS2 and DORA. We invite you to have a friendly, no-pressure conversation with our experts to see how we can strengthen your defences. We speak with the clarity of experts who want to simplify complex concepts for your benefit.
Don’t leave your business resilience to chance. Start your journey toward a data-centric fortress today. Contact Cornerstone for a Zero Trust Consultation and let’s build a secure, reliable future together. We’re proud of our regional roots and even prouder of the success we help our clients achieve.
Take the Next Step Toward Verified Resilience
Securing your business in 2026 requires more than just better tools. It demands a fundamental shift in how you view every identity and device on your network. By focusing on the six pillars of security and moving away from the illusion of a safe perimeter, you’ve already started the vital work to protect your team’s future. A professional zero trust assessment provides the data-driven roadmap you need to justify security spend and meet strict compliance standards with total confidence.
As a multi-award-winning IT provider and proud partner of industry leaders like Microsoft, IBM, and Cisco, we’re here to help you navigate this transition. We offer UK-wide professional support that combines world-class expertise with the approachable face of a local team. Let’s work together to turn your security into a proactive fortress that supports your long-term growth and emotional security.
Book Your Zero Trust Security Consultation Today and let’s start a conversation about your business stability. We’re looking forward to helping you lead with confidence.
Frequently Asked Questions
How long does a Zero Trust assessment typically take?
A standard zero trust assessment typically takes between one and two weeks to complete. The exact timeframe depends on the size of your digital environment and the number of users or devices we need to map. We focus on delivering a thorough report without disrupting your daily operations; ensuring you get a clear roadmap for improvement quickly and efficiently.
Do I need to be using Microsoft 365 to run a Zero Trust assessment?
You don’t need to be on Microsoft 365; although it offers excellent native tools for implementation. We work with a variety of platforms and can assess your security regardless of your current software stack. Our team has deep expertise in Cisco and IBM environments, so we can tailor the audit to your specific infrastructure and business needs.
Is Zero Trust only for large enterprises or does it apply to SMEs?
Zero Trust is essential for businesses of all sizes, especially as 70% of medium-sized UK firms faced attacks in the last year. Smaller organizations are often seen as easier targets by cybercriminals. We scale our approach to fit your business, providing the same high-level protection used by global enterprises but customized for a local SME’s budget and operational style.
What is the difference between a standard cyber audit and a Zero Trust assessment?
A standard audit often focuses on whether your firewall is active or if you’ve ticked specific compliance boxes. A zero trust assessment goes much deeper by assuming your perimeter has already been breached. It evaluates how you verify every single access request, ensuring that your security is data-centric rather than just network-based.
Can a Zero Trust assessment help with NIS2 or GDPR compliance?
Yes, it’s a powerful tool for meeting strict NIS2, DORA, and GDPR requirements. These regulations demand that you have robust, verifiable controls over who accesses your data. Our assessment provides the documented evidence you need to prove compliance to regulators and your board, showing that you’ve taken proactive steps to protect sensitive information.
How often should my business perform a Zero Trust assessment?
We recommend performing a full zero trust assessment at least once a year. You should also trigger a review if you make significant changes to your infrastructure, such as migrating to a new cloud platform or adopting a permanent hybrid work model. Regular checks ensure your defences evolve alongside new threats and that your configurations haven’t drifted from best practices.
What are the most common “red flags” found during an assessment?
The most common issues we find are a lack of phishing-resistant MFA and accounts with excessive permissions. We also frequently spot legacy systems that haven’t been properly isolated from the rest of the network. Identifying these “red flags” early allows us to implement quick wins that immediately lower your risk profile and strengthen your overall resilience.
Will implementing Zero Trust make it harder for my employees to work?
Implementing these principles actually makes work easier for your team. Modern Zero Trust tools use single sign-on (SSO) and seamless authentication, reducing the number of passwords your staff need to remember. By verifying device health in the background, we allow your employees to work securely from any location without facing frustrating technical barriers.
Posted on: July 12th, 2026 by Cornerstone
UK companies are currently facing an average of 1,988 cyberattacks every single day. It’s a sobering statistic that highlights why simply “having” the cloud isn’t the same as being truly protected. If you feel overwhelmed by complex admin menus or worry that a single data breach could damage your hard-earned reputation, you aren’t alone. Many local leaders find the sheer volume of security settings exhausting. However, mastering microsoft 365 security best practices uk standards doesn’t have to be a headache. It’s about moving from a “set and forget” mindset to a proactive, managed configuration that stands up to 2026’s AI-powered threats.
We agree that your focus should be on running your business, not decoding technical manuals. You deserve the peace of mind that comes from knowing your data is safe. This guide promises to strip away the confusion and provide a clear, NCSC-aligned roadmap to secure your operations. We’ll explore the essential configurations that reduce ransomware risks, clarify which licenses actually offer the best protection, and ensure you stay compliant with the latest UK data laws. By the end of this article, you’ll have the confidence to turn your digital workspace into a resilient fortress.
Key Takeaways
- Understand the 2026 threat landscape and why AI-powered phishing makes a robust security configuration more critical than ever for UK firms.
- Master the microsoft 365 security best practices uk organisations rely on by following the NCSC’s latest framework for secure cloud configurations.
- Evaluate the security gap between Microsoft 365 Business Standard and Premium to ensure your chosen license provides the protection your data deserves.
- Implement five essential security steps, from phishing-resistant MFA to automated device management, to proactively reduce your risk of ransomware.
- Discover why shifting from a DIY setup to a managed security partnership offers the long-term stability and expert support your business needs to grow safely.
The UK Cyber Threat Landscape for Microsoft 365 in 2026
UK companies currently face an average of 1,988 cyberattacks every single day. According to the Cyber Security Breaches Survey published in April 2026, 43% of UK businesses reported a breach in the last year. This figure rises to 65% for medium sized firms. These aren’t just global trends; they are local realities affecting businesses in our own communities. Microsoft 365 is the primary target because it holds the keys to your financial data, client lists, and internal communications. Relying on a reactive “break-fix” approach is no longer sustainable. You need a proactive strategy built on recognized information security standards to keep your operations running smoothly.
The Rise of AI-Driven Phishing in the UK
Attackers are now using generative AI to craft incredibly convincing emails that mimic local UK dialects and specific business contexts. In 2026, Business Email Compromise (BEC) is defined as a highly targeted attack where criminals use AI-generated deepfakes or perfectly written messages to impersonate trusted partners and divert business payments. Traditional spam filters often fail to catch these because they lack the obvious spelling errors or awkward phrasing of the past. Relying on basic filters alone is no longer a sufficient defence for your team.
The Impact of Downtime on Business Continuity
Technical security is vital, but emotional security matters just as much. As a business owner, you need to sleep soundly knowing your systems won’t vanish overnight. Ransomware was present in 48% of all data breaches in 2026, often leading to days or even weeks of total paralysis. The hidden costs of this downtime go far beyond the ransom itself. They include lost productivity, missed deadlines, and the immense stress of rebuilding your digital infrastructure from scratch. Our cyber security services focus on preventing this chaos before it starts. By adopting a robust microsoft 365 security best practices uk roadmap, you protect both your bottom line and your team’s peace of mind.
Aligning with the NCSC Secure Configuration Blueprint
The National Cyber Security Centre (NCSC) provides a definitive roadmap called the Secure Configuration Blueprint. While originally designed for government bodies, its latest version (Version 3.0) is a vital resource for any local business aiming to implement microsoft 365 security best practices uk experts recommend. It moves away from generic advice and offers a tiered “Good, Better, Best” framework. Most SMEs should aim for “Better” as a starting point. This level aligns closely with the Cyber Essentials scheme, which was updated in April 2026 to require all critical vulnerabilities to be patched within 14 days. Achieving this certification isn’t just about ticking boxes; it’s a powerful way to prove to your customers that their data is in safe, capable hands.
In the past, security was about building a wall around your office network. In 2026, that wall has disappeared. Your staff work from home, on the road, and in the cloud. This makes identity the new security perimeter. If a criminal steals a password, they are effectively inside your building. Shifting your focus to identity management ensures that only the right people have access to your sensitive information, regardless of where they are working. It’s a proactive shift that follows global information security standards while remaining grounded in the practical needs of a growing UK firm.
Identity and Access Management (IAM) Essentials
Passwords alone are a relic of the past. Today, we use Microsoft Entra ID to provide a sophisticated layer of verification that looks at more than just a string of characters. It evaluates the user’s location, the health of their device, and the sensitivity of the data they’re trying to reach. To meet the NCSC recommendation for administrative account protection, you must ensure that admin accounts are never used for day-to-day tasks like checking email or browsing the web. This simple separation of duties drastically reduces the chance of a high-level breach. If you’re curious about how your current setup measures up, our local team is always happy to help with a quick assessment.
Zero Trust Architecture for UK Businesses
Zero Trust might sound like a harsh term, but it’s actually a very reassuring concept for business owners. It follows a “never trust, always verify” mindset. Instead of assuming everything inside your network is safe, every single request is checked for legitimacy. This prevents a small breach in one area from spreading across your entire company. This architecture is a foundational part of modern cloud solutions that prioritize both growth and resilience. By adopting these microsoft 365 security best practices uk businesses can ensure that even if one account is compromised, the rest of the organization remains shielded.
Microsoft 365 Business Standard vs. Premium: The Security Gap
As of July 2026, the cost of Microsoft 365 Business Standard has increased to approximately £10.75 – £11.70 per user. Meanwhile, Business Premium pricing remains stable at around £16.90 – £18.60. This narrowing price gap makes the upgrade more compelling for local firms than ever before. While Standard provides the essential tools to get the job done, it lacks the advanced protection required to defend against 2026’s sophisticated attacks. Choosing Premium is the most effective way to adopt the microsoft 365 security best practices uk SMEs need for genuine resilience. It isn’t just an expense; it’s an investment in your company’s survival.
One of the biggest differences lies in device management. Microsoft Intune, which is included in the Premium tier, allows you to secure company data on personal phones and laptops. If an employee leaves or a device is lost in the local high street, you can remotely wipe only the business data without touching their personal photos. This balance of privacy and protection is essential for modern business continuity. When you compare the small monthly cost difference to the average financial impact of a breach, the return on investment for Premium is clear. It provides the automated investigation and response capabilities that smaller teams simply don’t have the time to manage manually.
Advanced Threat Protection (ATP) Explained
Defender for Business in the Premium tier introduces Safe Links and Safe Attachments. These tools scan every link and file in real-time, even if they’ve already landed in your inbox. If a link becomes malicious an hour after the email arrives, Premium blocks it instantly. This automated response reduces the burden on your team to be perfect every time they click. Any successful microsoft 365 security best practices uk strategy should start with the right foundation, which is why a Microsoft 365 migration should always include a full security audit to ensure your license tier matches your risk profile.
Information Protection and Data Loss Prevention (DLP)
Protecting sensitive UK client data is a legal requirement under the Data (Use and Access) Act 2025. Business Premium uses sensitivity labels to classify and protect files based on their content. For example, Data Loss Prevention (DLP) policies can automatically detect and block the accidental sharing of National Insurance (NI) numbers or financial details via email. This doesn’t slow your team down; it provides a safety net that catches human error before it becomes a breach. It allows your staff to work productively while you maintain the highest standards of data integrity.
5 Critical Security Steps Every UK Firm Should Take
Securing your digital environment doesn’t have to be an overwhelming task. By focusing on a few high-impact changes, you can significantly reduce your risk profile. These five steps form the backbone of microsoft 365 security best practices uk businesses use to stay resilient in 2026. They align with the NCSC’s Secure Configuration Blueprint and provide a clear path toward Cyber Essentials compliance. Taking these steps proactively ensures your team can work safely from anywhere without compromising your sensitive data.
- Enforce Phishing-Resistant MFA: Move beyond basic passwords and SMS codes to more secure methods like the Microsoft Authenticator app or FIDO2 security keys.
- Secure Every Endpoint: Use Microsoft Intune to manage every laptop, tablet, and smartphone that accesses your data, ensuring they meet your security standards before they connect.
- Apply the Principle of Least Privilege (PoLP): Limit administrative access to only those who absolutely need it, and ensure they use standard accounts for their daily work.
- Enable Audit Logging: Configure your system to record activity across your environment. This allows for proactive monitoring and provides a vital trail if an incident occurs.
MFA: The Single Most Effective Defence
In 2026, SMS-based multi-factor authentication is no longer considered a reliable barrier. Attackers can easily bypass it through SIM swapping or interception. Transitioning your team to the Microsoft Authenticator app or hardware-based FIDO2 keys is a critical upgrade. Conditional Access is a set of rules that determines whether a user is granted access based on their location, device health, and risk level. By implementing these microsoft 365 security best practices uk leaders can ensure that a stolen password isn’t enough to compromise the entire firm.
Securing the Mobile Workforce
The rise of remote work has made “Bring Your Own Device” (BYOD) a standard practice, but it also introduces significant risks. Without proper management, a lost personal phone could mean a major data breach. Microsoft Intune allows you to separate business and personal data, giving you remote wipe capabilities to protect company information if a device goes missing. Managing this hardware effectively requires robust it company solutions that integrate seamlessly with your security posture. If you’re unsure if your current mobile policy is “secure enough,” reach out for a proactive security review with our local experts today.
Why Managed Security is the Proactive Choice for 2026
Managing your own digital defences can feel like a full-time job you never actually applied for. In 2026, the technical landscape moves at lightning speed. A “set and forget” approach to your cloud environment simply isn’t enough to stop modern, AI-driven threats. While the settings we’ve discussed are vital, the real challenge lies in keeping those configurations updated as new vulnerabilities emerge. This is where moving from a DIY mindset to a managed security model makes all the difference for a growing firm. It shifts the burden of constant vigilance from your shoulders to a team of dedicated experts.
As a multi-award-winning UK IT provider and Microsoft partner, we believe that security should be a foundational element of your business stability. We don’t just look at support as a transactional service. Instead, we aim to be your long-term technology partner. By implementing microsoft 365 security best practices uk organisations can trust, we ensure your systems are resilient enough to handle whatever the future holds. This collaborative approach means we work alongside you to understand your specific goals, tailoring our microsoft 365 security best practices uk roadmap to fit your unique regional roots and operational needs.
Beyond the Settings: Proactive Monitoring
Real-time alert monitoring is the difference between stopping a breach in its tracks and discovering a disaster weeks too late. Our managed services provide continuous oversight of your environment, catching suspicious login attempts or unusual data movements the moment they happen. We also provide regular security audits and compliance reporting to ensure you’re always meeting the latest UK data protection standards. This proactive stance allows you to stop worrying about technical glitches and focus entirely on your business growth. You gain the freedom to lead, backed by the emotional security of a protected workspace.
Your Invitation to a Security Conversation
Every bespoke security solution starts with a simple, expert-led discussion. We pride ourselves on offering professional authority with a sense of regional warmth that makes complex tech feel approachable. We’re a local team that understands the challenges faced by UK SMEs because we live and work in the same communities. Our promise is to provide the clarity and reliability you need to feel confident in your digital future. We’d love to hear about your current setup and explore how we can strengthen your posture together. We invite you to start a conversation with one of our specialists today to see how we can build a more resilient business for 2026 and beyond.
Building a Resilient Foundation for Your UK Business
As a multi-award-winning UK IT services provider and certified partner for both Microsoft and Cisco, we specialize in bespoke technology solutions designed for growth. We believe in providing more than just technical support; we offer the emotional security that comes from a dedicated partnership. You don’t have to navigate these complex security menus alone. Secure your business with a multi-award-winning partner, let’s talk about your Microsoft 365 security today. Our local team is ready to help you grow with absolute confidence.
Frequently Asked Questions
Is Microsoft 365 security included in my basic subscription?
Foundation security is included in every subscription, but basic levels often lack the advanced tools needed for 2026 threats. While you get standard anti-spam and basic multi-factor authentication, features like automated threat investigation and remote device wiping are reserved for higher tiers. Relying on basic settings alone can leave your business vulnerable to sophisticated phishing attacks that bypass standard filters.
What is the most common Microsoft 365 security mistake UK businesses make?
The most frequent error is failing to move beyond default “out of the box” settings. Many firms don’t enforce phishing-resistant MFA or block legacy authentication, which accounts for a significant portion of successful breaches. Implementing microsoft 365 security best practices uk leaders recommend means actively closing these gaps through custom policies that reflect your specific risk profile and operational needs.
Does Microsoft 365 comply with UK GDPR requirements?
Microsoft 365 provides the necessary infrastructure for compliance, but the responsibility for correct configuration lies with your business. You must ensure that sensitivity labels and data loss prevention policies are active to meet the standards set by the Data (Use and Access) Act 2025. Properly managed settings allow you to control data residency and access, ensuring you meet your legal obligations to protect client information.
How often should my business perform a Microsoft 365 security audit?
We recommend conducting a full security audit at least every quarter to stay ahead of evolving threats. Regular reviews are essential for identifying inactive accounts, checking for “Shadow AI” usage, and ensuring your configurations still align with the latest NCSC guidance. This proactive rhythm helps you catch minor vulnerabilities before they can be exploited by attackers targeting UK SMEs.
Can I secure Microsoft 365 without hindering my employees’ productivity?
You can definitely maintain a high level of security without slowing your team down. By using Conditional Access, you only require extra verification when a login attempt appears risky, such as from an unrecognized device or location. This creates a seamless experience for your staff during their normal workday while keeping a robust shield in place behind the scenes.
What happens if a UK business suffers a data breach in Microsoft 365?
You are legally required to report significant breaches to the Information Commissioner’s Office (ICO) within 72 hours. Beyond potential fines, a breach often leads to expensive downtime and long-term damage to your professional reputation. Having a managed security plan ensures you have the audit logs and recovery protocols needed to respond quickly and minimize the impact on your business continuity.
Is Cyber Essentials certification required for UK government contracts?
Cyber Essentials is now a mandatory requirement for the vast majority of UK government and public sector contracts. The certification process was updated in April 2026 to include stricter rules on vulnerability patching and device management. Aligning your microsoft 365 security best practices uk with these standards is a practical way to prove your reliability to both the government and private sector clients.
How does Microsoft 365 Business Premium improve my security over Standard?
Business Premium introduces enterprise-grade tools like Microsoft Intune and Defender for Business that are missing from the Standard tier. These features allow you to manage every device that accesses your data and provide automated responses to detected threats. This extra layer of protection is increasingly seen as the minimum viable security baseline for local businesses operating in a high-risk digital landscape.